
Course 47 - SCADA Security Architect (CSSA) | Episode 9: Protocols & Wireless Exploitation
· 26 min
Show notes
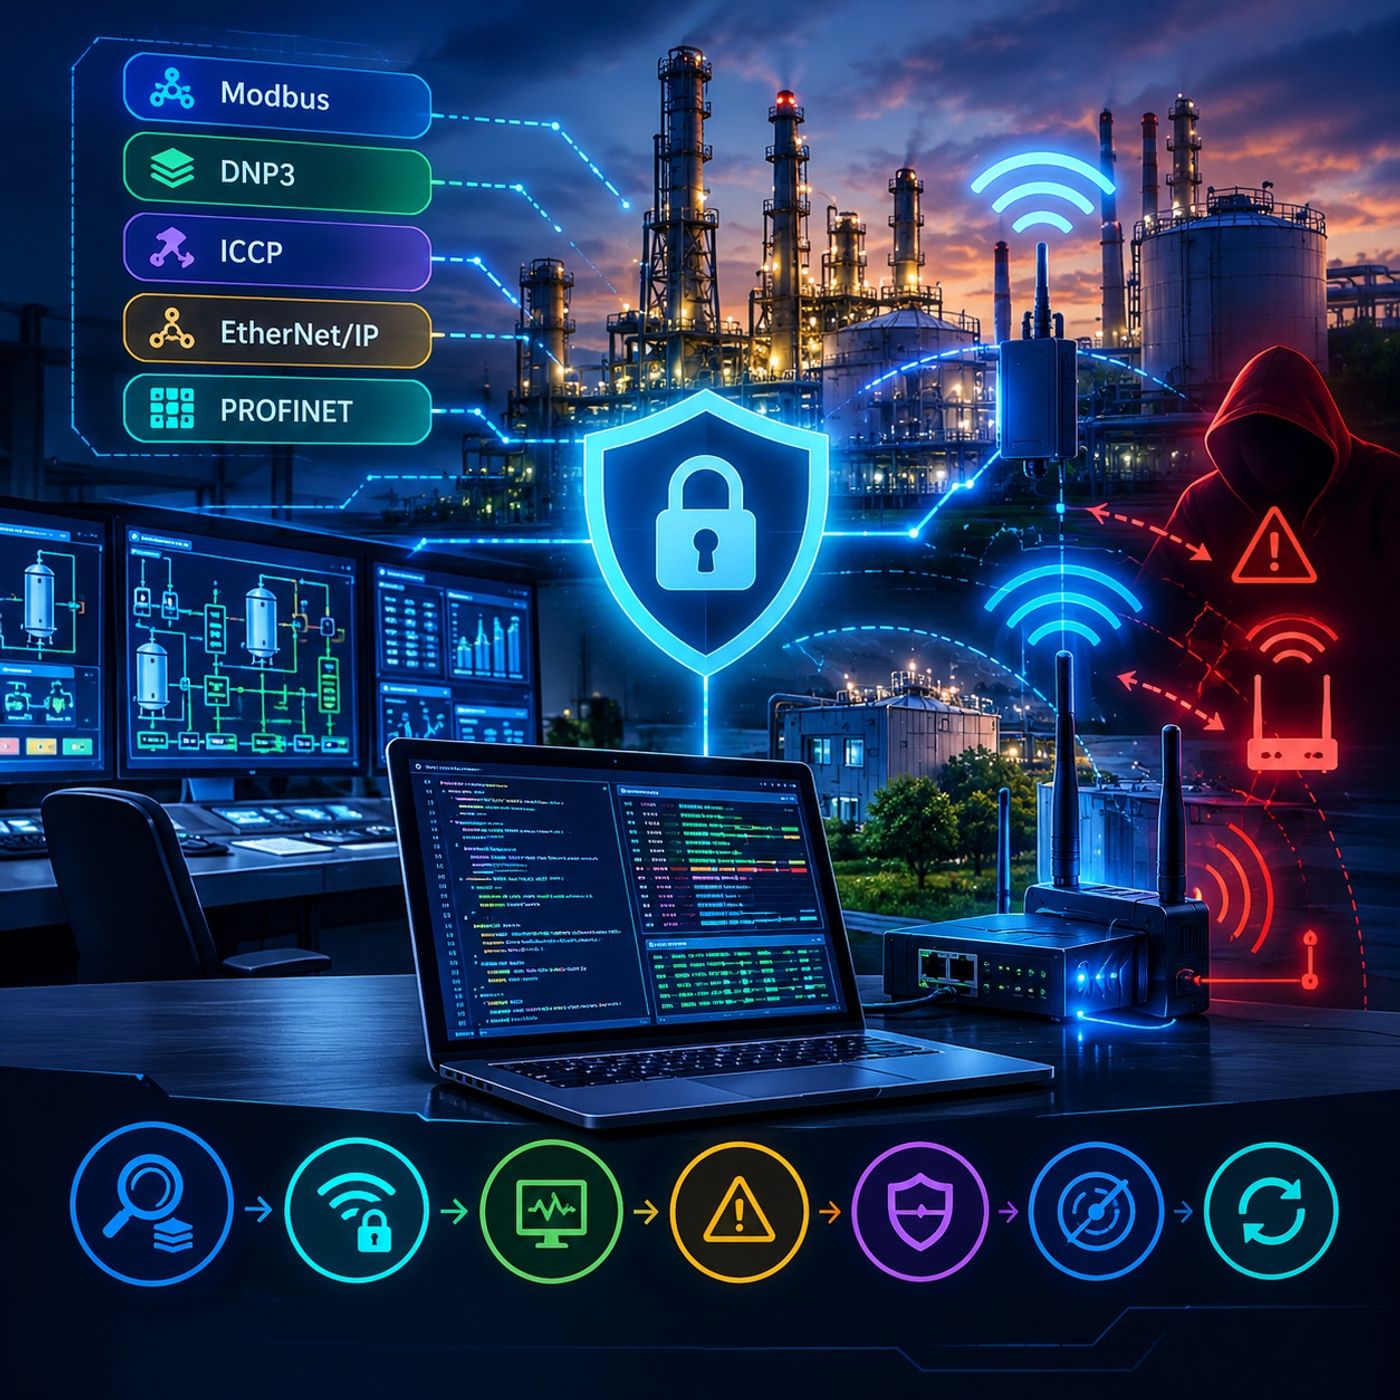
ICS Security: SCADA Protocols & Wireless VulnerabilitiesEpisode OverviewThis episode examines security weaknesses in industrial communication protocols and wireless infrastructure supporting Industrial Control Systems (ICS) and SCADA environments. It explores protocol-level vulnerabilities, fuzz testing, man-in-the-middle risks, wireless authentication weaknesses, and network disruption threats, with an emphasis on safe assessment and effective defensive controls.Key Topics Covered1. Industrial Protocol Security
• Understanding security considerations in Modbus, DNP3, ICCP, EtherNet/IP, and PROFINET.
• Identifying risks associated with legacy protocols, insufficient authentication, and limited message-integrity protections.
• Exploring protocol fuzzing and controlled testing to uncover unexpected behavior and implementation flaws.
• Examining man-in-the-middle attacks and the importance of network segmentation, secure gateways, and protocol-aware monitoring.
2. Industrial Wireless Security
• Understanding wireless risks in industrial networks and connected operational devices.
• Comparing legacy WEP security with WPA and WPA2, including the importance of modern, securely configured wireless protections.
• Assessing rogue access points, unauthorized devices, and insecure wireless configurations.
• Examining wireless jamming and packet injection as potential threats to communications availability and integrity.
3. Assessment and Defensive Strategies
• Identifying exposed industrial protocols and wireless attack surfaces.
• Using passive monitoring and controlled testing to investigate weaknesses.
• Restricting access to industrial networks through segmentation, firewall rules, and secure remote-access mechanisms.
• Strengthening wireless authentication and encryption, monitoring for rogue devices, and preparing for communication disruptions.
• Coordinating all active testing with OT operators to protect system safety and availability.
Key Takeaways
• Legacy industrial protocols may lack security protections expected in modern enterprise networks.
• Protocol fuzzing and traffic analysis can help identify implementation and configuration weaknesses.
• Weak wireless configurations can expose industrial communications to interception, unauthorized access, and disruption.
• Segmentation, secure authentication, encryption, and continuous monitoring provide complementary layers of defense.
• Testing must be explicitly authorized and designed around the safety and reliability requirements of industrial operations.
Security Workflow: Identify Protocols → Assess Wireless Exposure → Analyze Traffic → Validate Weaknesses → Strengthen Controls → Monitor → Retest
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
Get the books of the CyberCode Academy podcast:
📚 The book series: 416 lessons, 12 books, hundreds of original diagrams: security, networking and…
Website: spreaker.com


