
From Upload to Root: Deconstructing PHP-to-Shell Exploitation Vectors🛡️
· 25 min · Avsnitt 47
Avsnittsbeskrivning
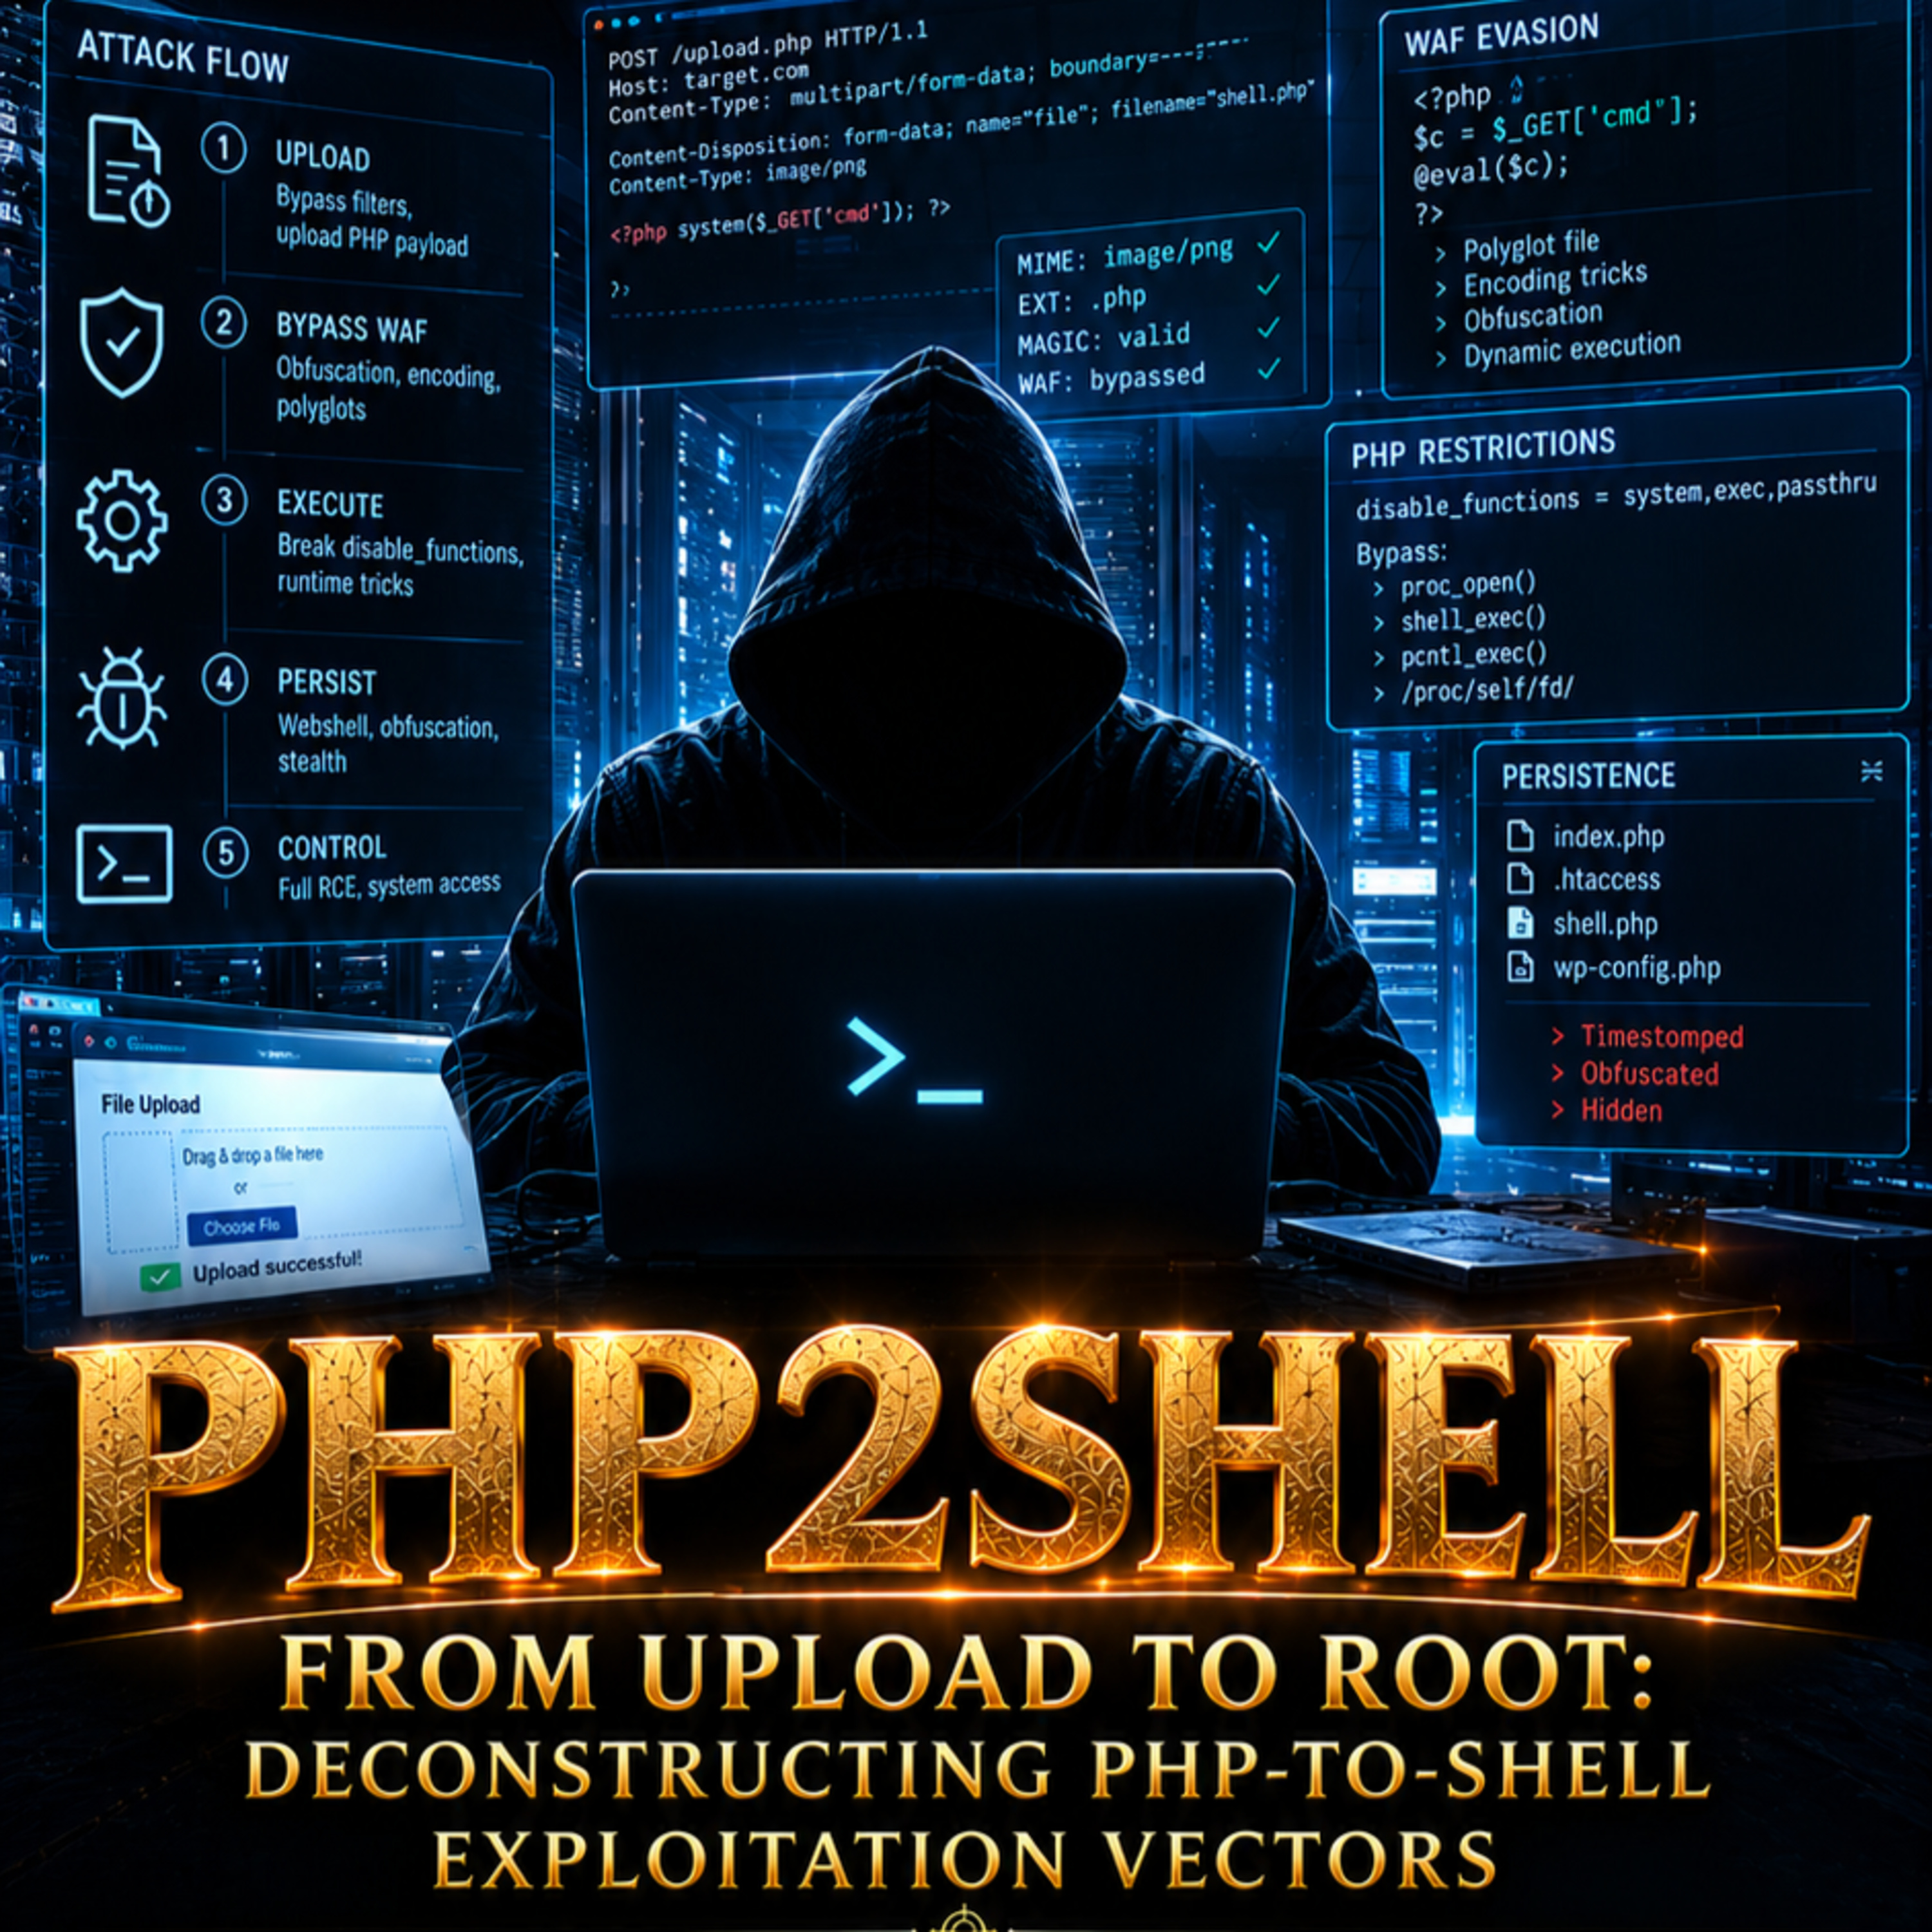
Web applications remain the most targeted surface in enterprise infrastructure.
Despite decades of secure coding standards, arbitrary file upload flaws that lead to Remote Code Execution (RCE) continue to breach production environments.
In this technical installment of the Robert Joodat Podcast, we dissect the exact engineering mechanics behind PHP2Shell vulnerabilities and examine how adversaries transform simple application flaws into fully interactive remote shells.
We strip away generic security advice to analyze real-world exploitation pathways.
We break down how threat actors bypass…
Webbplats: podcasters.spotify.com


