
Show notes
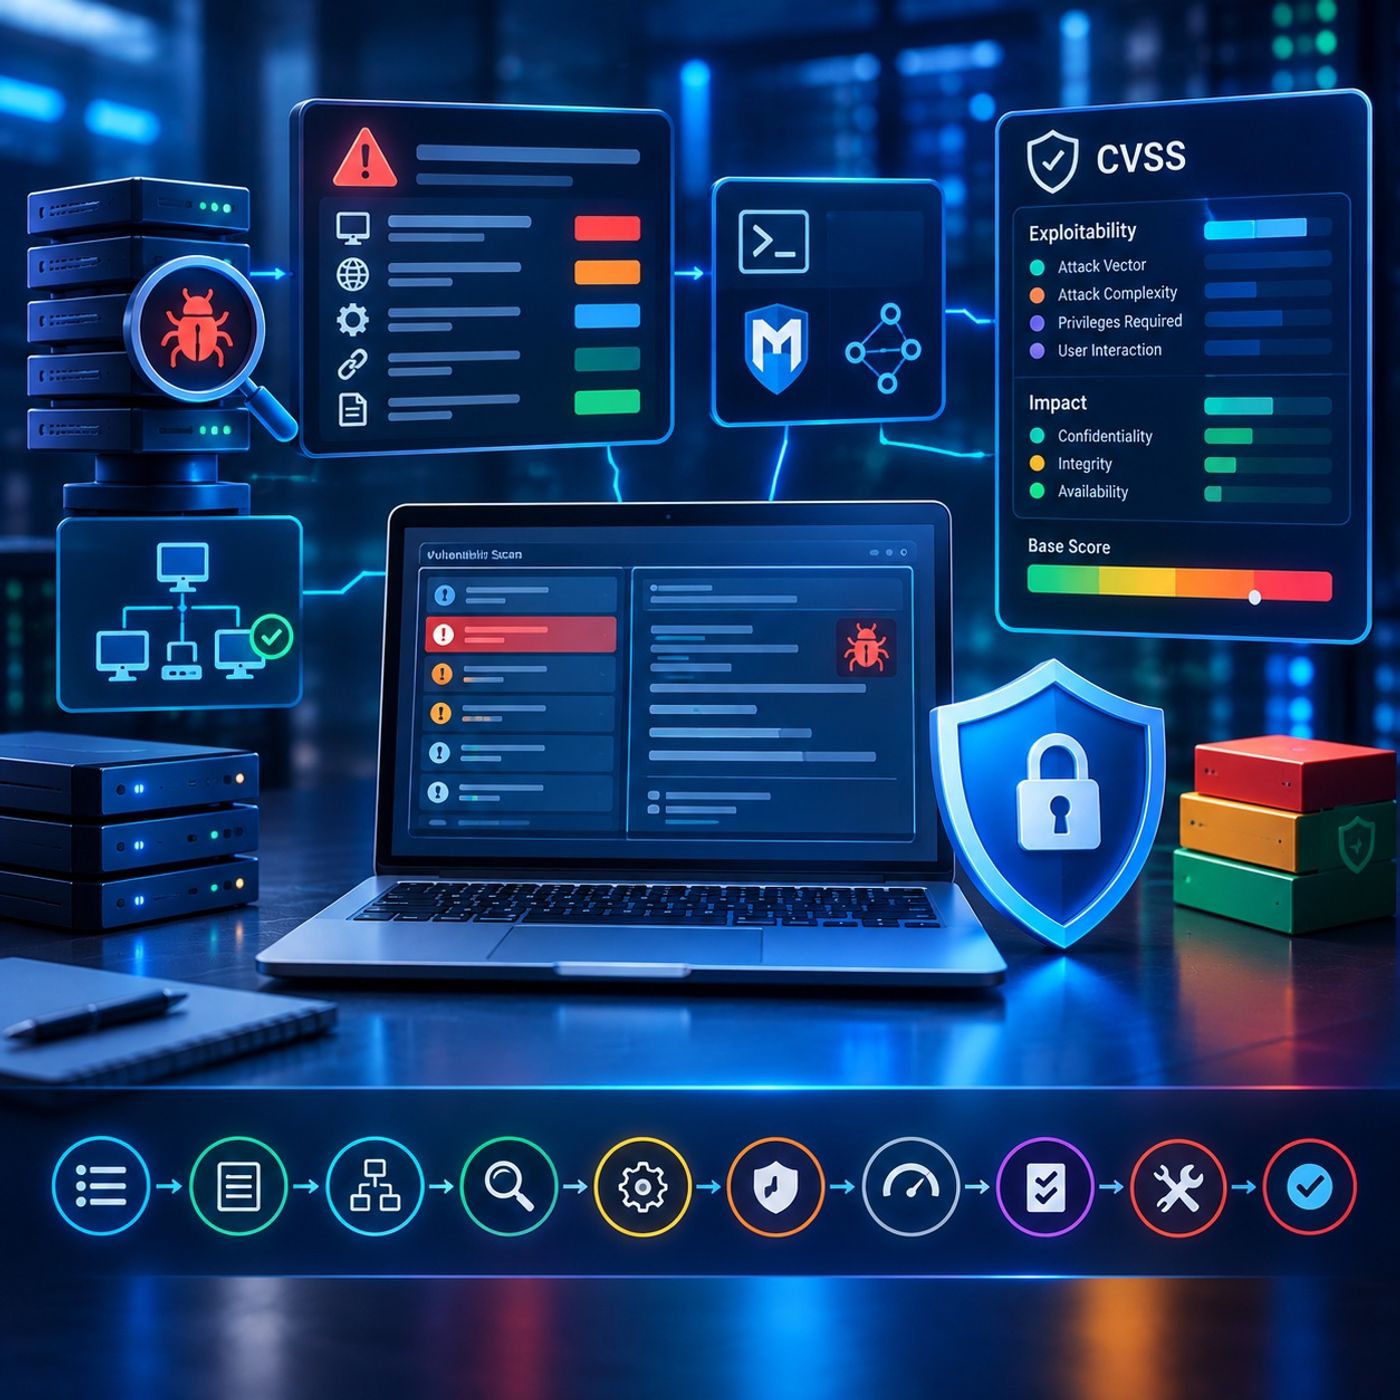
Episode OverviewThis episode provides a structured guide to vulnerability management, showing how security analysts move from raw vulnerability scanner findings to validated vulnerabilities and standardized risk ratings.The episode begins with the practical interpretation of scanner reports, using tools such as Nessus to examine vulnerability descriptions, affected hosts, exploitability information, and supporting references. It then explores how analysts investigate the underlying cause of a finding, assess whether exploitation is feasible, identify relevant exploitation frameworks such as Metasploit, and isolate affected systems for controlled remediation.The episode then introduces the Common Vulnerability Scoring System (CVSS), explaining how standardized metrics describe the characteristics and potential impact of a vulnerability. The discussion covers exploitability factors such as attack vector, attack complexity, and authentication requirements, alongside the confidentiality, integrity, and availability impacts used to evaluate consequences.Finally, the episode examines how CVSS base scores are calculated and how the resulting numerical score is mapped to standardized severity categories.Key Topics Covered1. Interpreting Vulnerability Scanner ReportsVulnerability scanners generate large volumes of technical findings, but scanner output alone does not constitute a complete risk assessment. Analysts must interpret and validate the information before determining the appropriate remediation strategy.Key report elements include:
• Vulnerability synopsis and summary
• Detailed technical descriptions
• Affected hosts and IP addresses
• Affected services, ports, or applications
• Exploitability information
• References to known vulnerabilities and security advisories
• Available exploitation or proof-of-concept references
• Recommended remediation actions
The analyst's role is to connect these technical findings to the actual systems and services affected.2. Root-Cause and Exploitability AnalysisAfter identifying a vulnerability, analysts investigate why the weakness exists and whether it can realistically be exploited in the affected environment.This may involve examining:
• Vulnerable software versions
• Missing security patches
• Configuration weaknesses
• Exposed network services
• Authentication requirements
• Available exploit techniques
• Existing security controls and compensating controls
Frameworks such as Metasploit may be relevant when validating exploitability in an explicitly authorized assessment or isolated security laboratory.3. Identifying and Isolating Vulnerable HostsScanner results can be used to identify the specific hosts affected by a vulnerability.A practical workflow includes:
• Review the scanner finding.
• Identify affected IP addresses or hostnames.
• Determine the vulnerable service or application.
• Validate the finding where appropriate.
• Assess the host's business and security context.
• Isolate or restrict the…
Website: spreaker.com
