
Course 46 - CompTIA Cybersecurity Analyst | Episode 18: Host & Network Security Essentials
· 22 min
Show notes
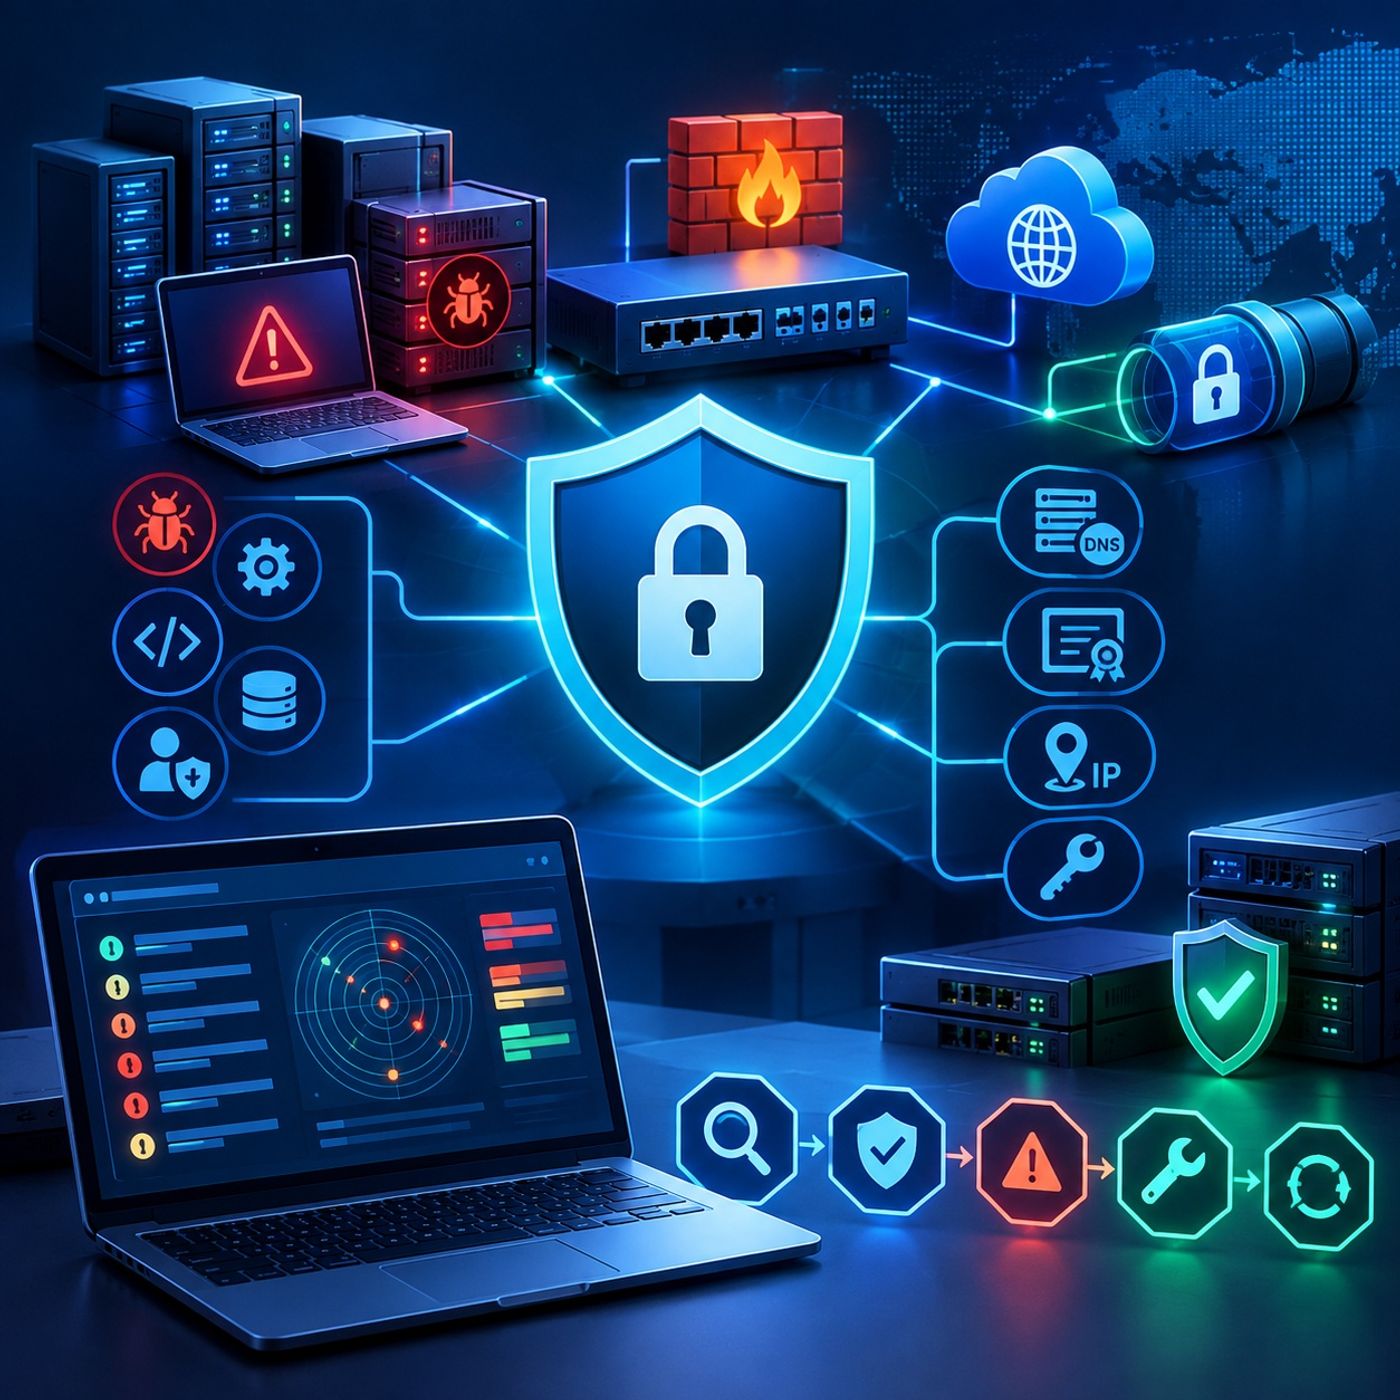
Episode OverviewThis episode provides a comprehensive examination of vulnerabilities affecting both host systems and network infrastructure, showing how outdated software, insecure configurations, vulnerable protocols, and missing patches can expose an enterprise to compromise.The discussion begins with host and server security, focusing on unsupported operating systems, software vulnerabilities, memory-safety issues, privilege escalation, debugging configurations, and unpatched systems. It then moves into network infrastructure, examining firmware management, secure administration, TLS security, certificate validation, DNS protection, information disclosure, and VPN security.Finally, the episode brings these concepts together through vulnerability-scanning and remediation workflows, demonstrating how tools such as Nessus and Qualys can help security teams identify weaknesses across endpoints and network devices.Key Topics Covered1. Host and Server VulnerabilitiesHost-based vulnerabilities can arise from outdated software, insecure configurations, missing patches, and excessive privileges.A major concern is the continued operation of unsupported or end-of-life operating systems and applications. Once vendors stop providing security updates, newly discovered vulnerabilities may remain permanently exposed unless the organization upgrades, replaces, or otherwise mitigates the affected technology.Key areas include:
- End-of-life operating systems and applications
- Missing security patches
- Vulnerable services and applications
- Insecure configurations
- Excessive privileges
- Debugging functionality left enabled
- Memory-safety vulnerabilities
- Privilege-escalation opportunities
2. Buffer Overflows and Memory-Safety RisksThe episode examines buffer overflows, a class of memory-safety vulnerability in which data exceeds the boundaries of an allocated memory region.Depending on the affected software and execution environment, memory corruption can potentially result in:
- Application crashes
- Unexpected program behavior
- Memory corruption
- Denial of service
- Arbitrary code execution
- Privilege escalation
The episode highlights the historical importance of memory-corruption vulnerabilities while emphasizing that precise prevalence statistics depend heavily on the dataset, time period, and definition of a breach.3. Privilege EscalationA vulnerability does not necessarily provide an attacker with the highest level of system access immediately.Privilege escalation involves obtaining permissions beyond those initially available.Security teams should therefore assess:
- Local user privileges
- Administrative accounts
- Service-account permissions
- SUID or equivalent privileged execution mechanisms
- Vulnerable privileged applications
- Operating-system security controls
- Separation of administrative and standard-user access
Effective privilege management limits the impact of a successful initial compromise.4. Debugging and Development…
Website: spreaker.com