
Course 46 - CompTIA Cybersecurity Analyst | Episode 25: Mastering Layered Defense & Security Controls
· 18 min
Note dell’episodio
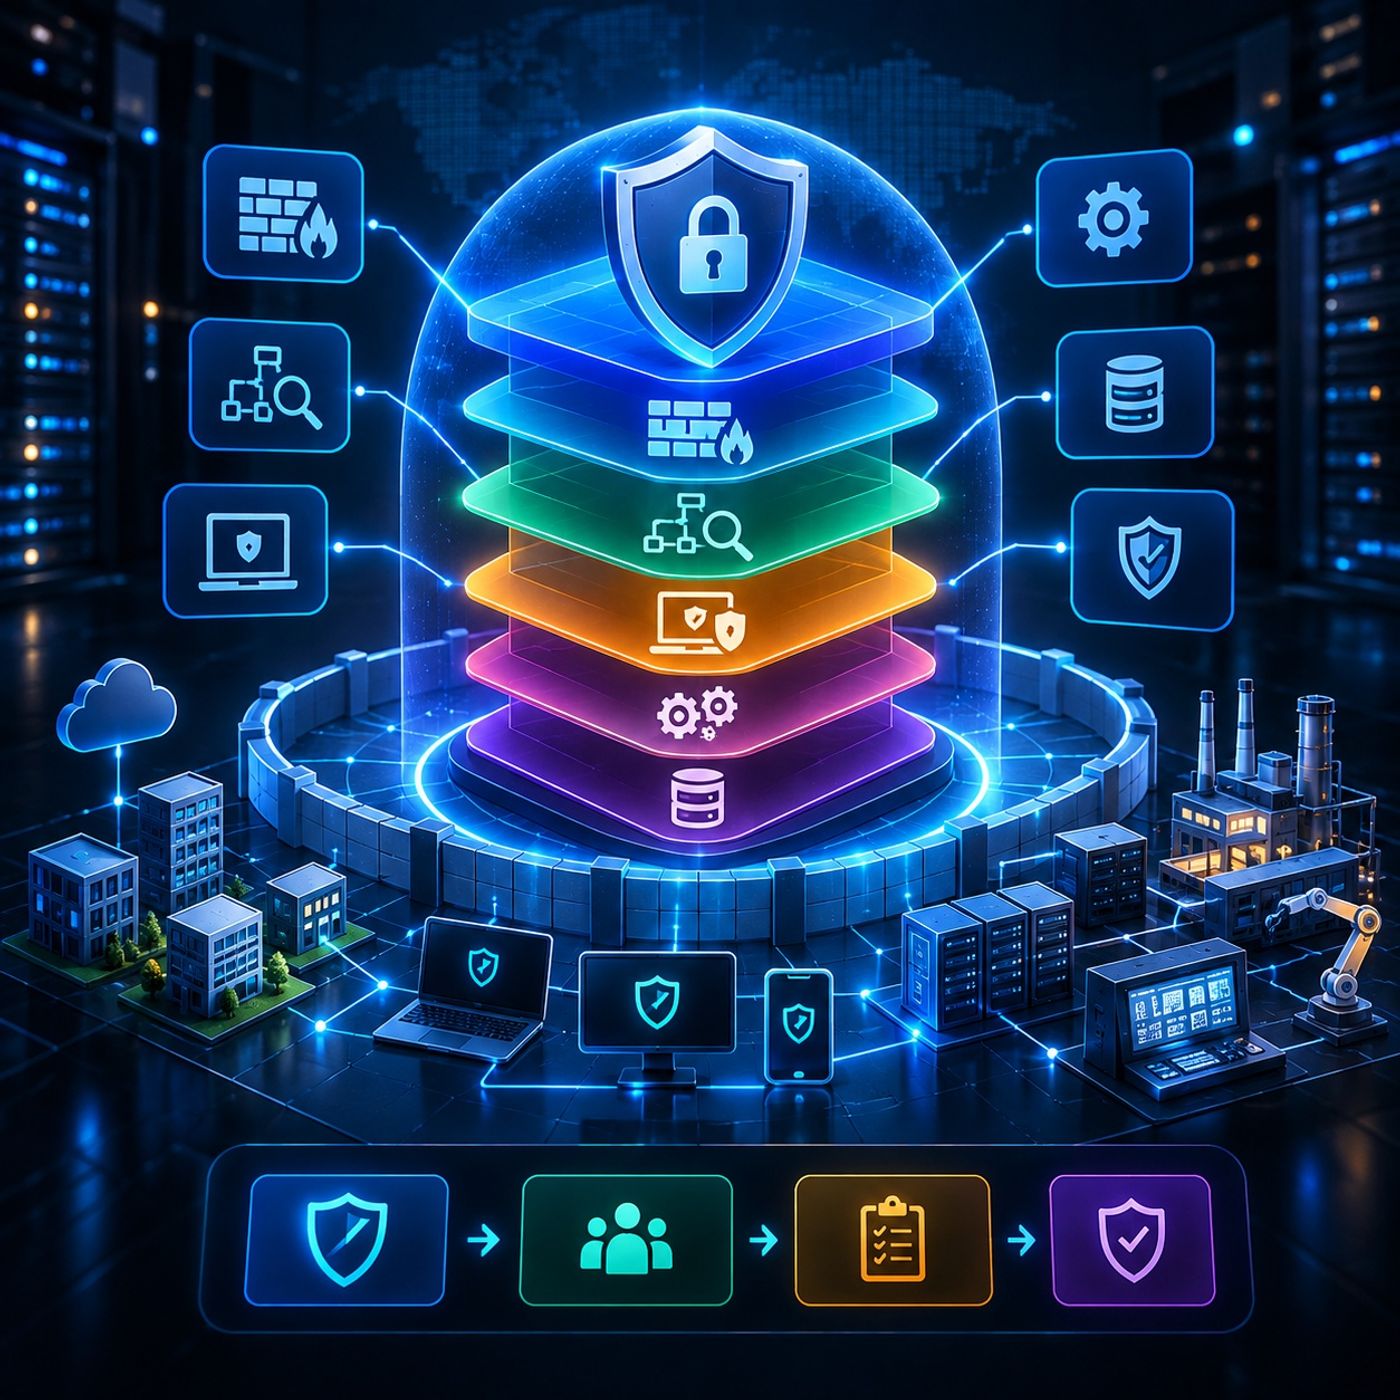
Frameworks for Network Security: Defensive Architectures and Security ControlsEpisode OverviewThis episode examines the fundamental frameworks used to build a resilient network security posture through defense in depth, layered security architectures, and security controls.It explores how organizations combine technical safeguards, administrative processes, and operational practices to reduce risk across networks, systems, applications, and sensitive information. The episode also emphasizes an important principle of security architecture: controls must provide meaningful protection without unnecessarily disrupting legitimate business operations.Key Topics Covered1. Defense in Depth
• Layered Security: Understand how multiple security layers work together so that the failure or bypass of one control does not automatically result in compromise.
• Perimeter Protection: Examine border routers, firewalls, and other network-edge controls used to regulate traffic entering and leaving an environment.
• Network Detection and Prevention: Explore IDS/IPS technologies for identifying and, where appropriate, blocking suspicious network activity.
• Endpoint Security: Incorporate endpoint protection, host-based controls, secure configurations, and patch management into the broader defensive architecture.
• Application Security: Maintain secure applications through vulnerability management, secure configuration, and timely security updates.
• Security vs. Business Operations: Balance protective controls with availability, usability, performance, and operational requirements to avoid creating security measures that unnecessarily interfere with legitimate business processes.
2. Layered Security Architecture ModelsThe episode examines several approaches for structuring defense-in-depth architectures:
• Uniform Protection: Apply a consistent baseline of security controls across assets where similar protection requirements exist.
• Protected Enclaves: Isolate particularly sensitive systems or environments—such as payment-card or critical-data systems—with additional controls and segmentation.
• Risk- or Threat-Based Architecture: Prioritize controls according to specific threats, attack paths, exposure levels, and organizational risk.
• Information Classification-Based Architecture: Match security protections to the sensitivity and classification of the information being processed or stored.
These approaches can also be combined. For example, an organization may apply a common security baseline everywhere while placing highly sensitive information inside additional protected enclaves.3. Security Controls by Implementation TypeSecurity controls can be categorized according to how they are implemented.Technical ControlsTechnology-based mechanisms that directly enforce or support security requirements, including:
• Firewalls
• Authentication and access-control systems
• Endpoint security and anti-malware technologies
• Network segmentation
• Encryption
• IDS/IPS
•…
Sito web: spreaker.com
