
Course 46 - CompTIA Cybersecurity Analyst | Episode 28: AAA Protocols, System Management, and Key Vulnerabilities
· 20 min
Note de episod
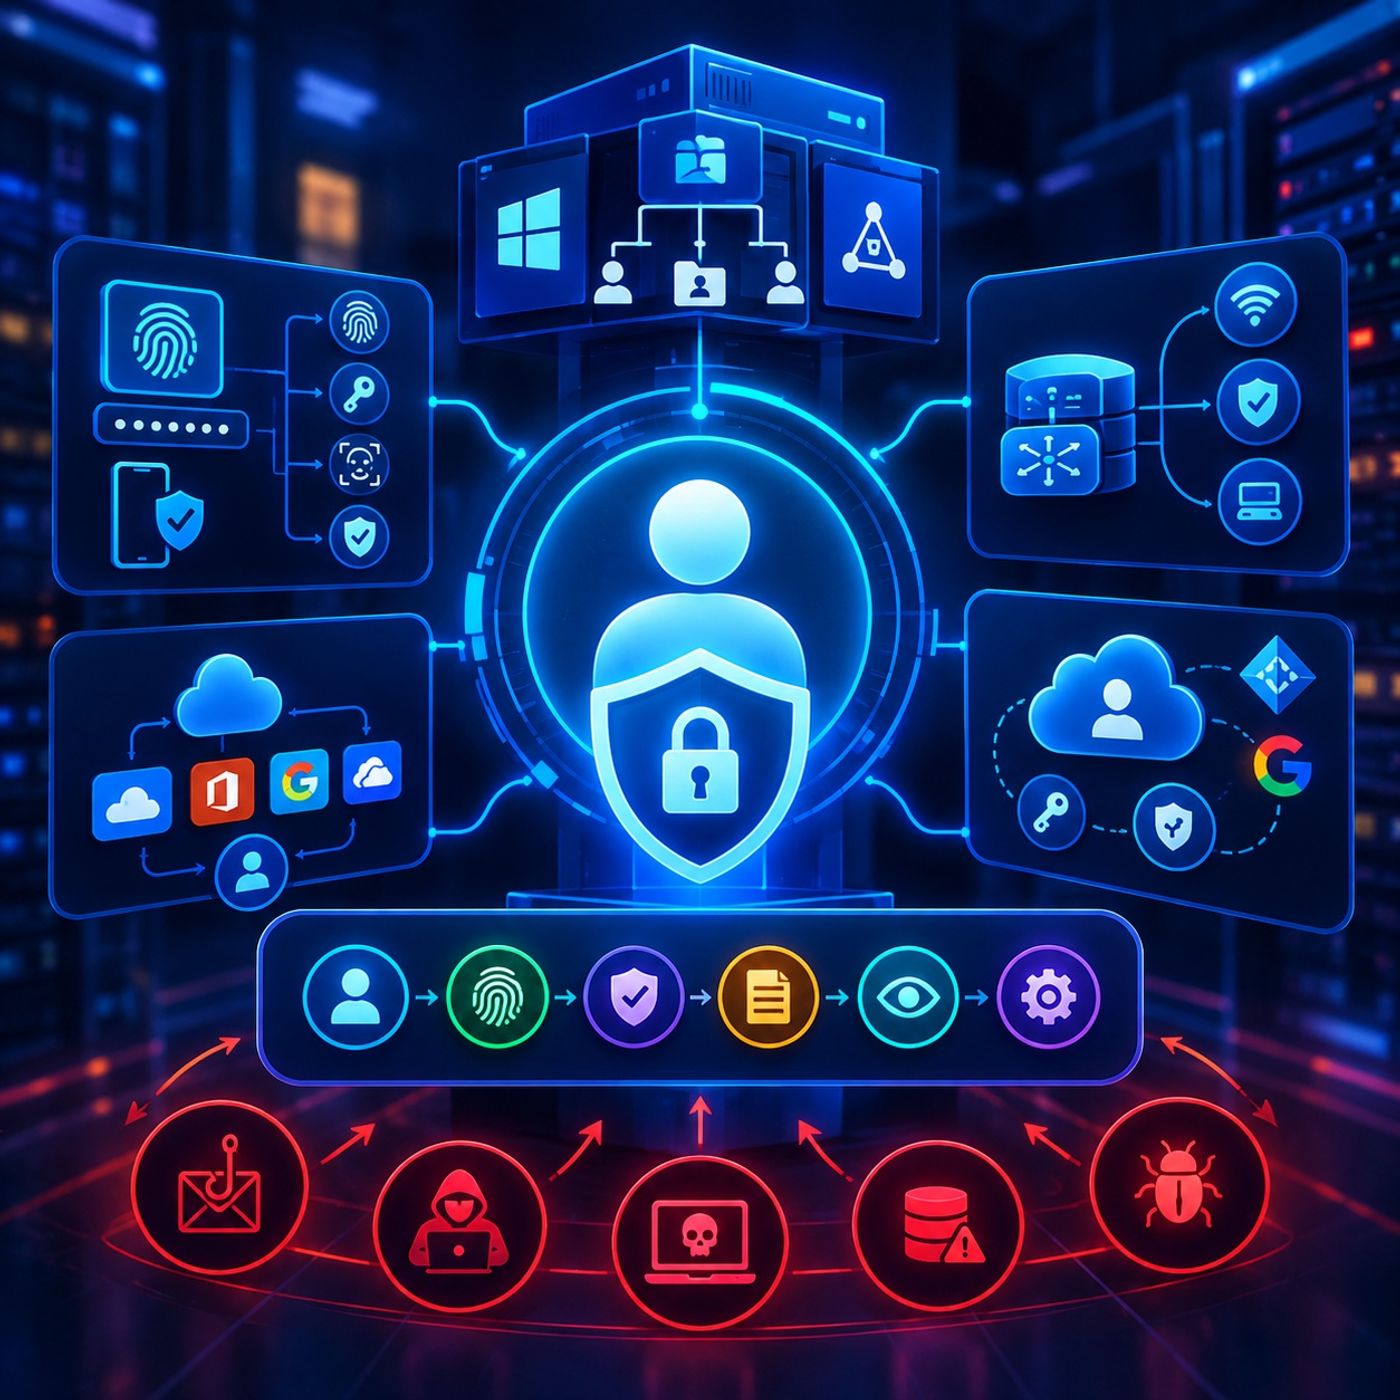
Identity Security Fundamentals: AAA, Directory Services, and Identity ThreatsEpisode OverviewThis episode provides a comprehensive introduction to digital identity, directory services, authentication protocols, and the security threats that target identity infrastructure.It begins with the fundamentals of establishing and managing digital identities, then explores the AAA framework—Authentication, Authorization, and Accounting. The episode continues into centralized directory architectures such as LDAP and Microsoft Active Directory, along with technologies that support centralized authentication, Single Sign-On, and federated identity. Finally, it examines common attack vectors targeting users, endpoints, applications, and identity configurations.Key Topics Covered1. Digital Identity Fundamentals and the Three A's
• Digital Identity: Understand how attributes, identifiers, credentials, and authentication factors contribute to establishing and validating a digital identity.
• Authentication: Determine whether a user, device, or service is genuinely the identity it claims to be.
• Authorization: Determine what an authenticated identity is permitted to access or perform.
• Accounting: Record and audit authentication, authorization, and other relevant activities to provide visibility and support investigations.
• Identity Lifecycle: Consider how identities are created, provisioned, modified, reviewed, disabled, and eventually removed.
• Least Privilege: Limit permissions to those necessary for an identity's legitimate responsibilities.
2. Directory Services and Identity ArchitectureCentralized directory services provide structured repositories for identities, groups, organizational information, and access-related data.
• LDAP: Explore the Lightweight Directory Access Protocol and its role in accessing and managing directory information.
• Microsoft Active Directory: Understand how Active Directory organizes users, computers, groups, and policies within domain-based environments.
• Organizational Units (OUs): Use hierarchical structures to organize objects and support administration and policy application.
• Access Control: Apply appropriately scoped ACLs and permissions to protect directory objects and administrative functions.
• Directory Encryption: Protect directory communications using secure transport mechanisms such as LDAP over TLS (LDAPS) or StartTLS where supported and properly configured.
• Credential Protection: Store passwords using modern, salted, slow password-hashing mechanisms rather than reversible encryption or obsolete hashing algorithms.
• Directory Hardening: Restrict administrative privileges, protect privileged accounts, monitor authentication activity, and minimize unnecessary exposure of directory services.
3. Network Authentication and Federated IdentityThe episode also examines technologies that extend centralized identity management across networks and applications.
• RADIUS: Explore the Remote Authentication Dial-In…
Site: spreaker.com
