
Course 46 - CompTIA Cybersecurity Analyst | Episode 29: Account Lifecycles, and Identity Exploits
· 16 min
Show notes
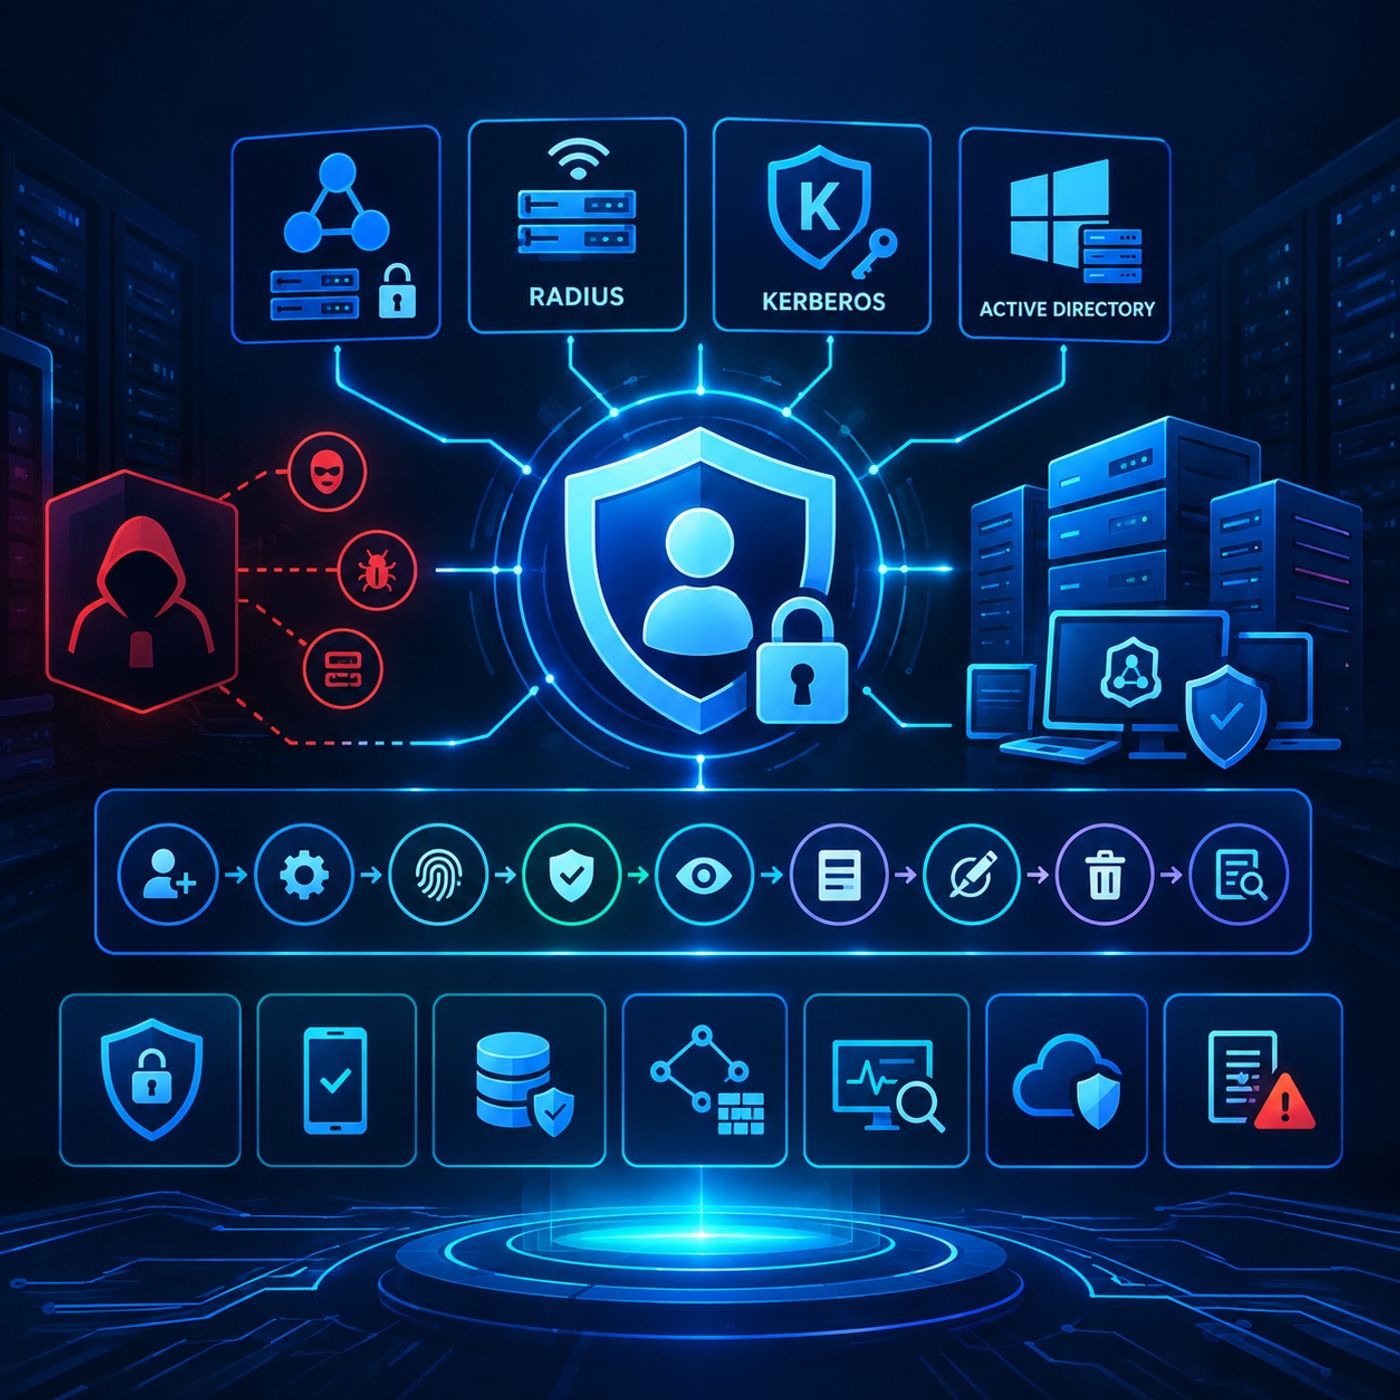
Securing Identity Systems: AAA Protocols, Account Lifecycles, and Identity ThreatsEpisode OverviewThis episode examines how attackers target identity infrastructure and the controls organizations can use to protect authentication, authorization, directory services, and privileged access.It explores the security considerations surrounding LDAP, RADIUS, Kerberos, and Microsoft Active Directory, including legacy authentication risks, credential theft, session attacks, and directory-service vulnerabilities. The episode then follows the user account lifecycle from initial creation through deprovisioning, showing how organizations can apply least privilege and prevent privilege creep as responsibilities change.Finally, it examines major identity-related attack categories—including impersonation, session hijacking, man-in-the-middle attacks, privilege escalation, and rootkits—and connects each threat to appropriate defensive controls.Key Topics Covered1. Securing AAA Protocols and Directory Services
• LDAP Security: Protect directory communications with TLS, enforce strong access controls, validate and safely handle application input, and prevent unauthorized directory queries or modifications.
• LDAP Injection: Understand how improperly constructed directory queries can allow attacker-controlled input to alter query behavior, and how input validation and parameterized query construction can reduce this risk.
• RADIUS Security: Protect authentication traffic using secure transport and network architecture appropriate to the deployment. Where RADIUS is transported across untrusted networks, mechanisms such as IPsec or modern RADIUS-over-TLS approaches can provide additional protection, depending on platform support.
• Kerberos: Protect Key Distribution Centers (KDCs), privileged accounts, service accounts, and authentication infrastructure against credential theft and ticket abuse.
• Active Directory: Harden domain controllers, reduce privileged-account exposure, monitor authentication activity, and retire legacy authentication protocols where organizational compatibility and platform support allow.
• Legacy Authentication: Understand the security risks associated with older mechanisms such as NTLM and the importance of moving toward stronger authentication approaches while carefully managing compatibility requirements.
2. Understanding Identity-Based Attacks
• Golden Ticket Attacks: Understand how compromise of the Active Directory KRBTGT account can enable forged Kerberos ticket attacks and why protecting domain controllers and privileged credentials is critical.
• Pass-the-Hash: Recognize how stolen password hashes can sometimes be abused for authentication without recovering the original plaintext password.
• Session Replay and Hijacking: Understand how stolen authentication tokens or session identifiers can allow an attacker to impersonate an already authenticated user.
• Impersonation: Examine attacks that exploit stolen credentials, compromised…
Website: spreaker.com


