
Course 46 - CompTIA Cybersecurity Analyst | Episode 31: Detecting Attacks and Managing Federated Systems
· 14 min
Show notes
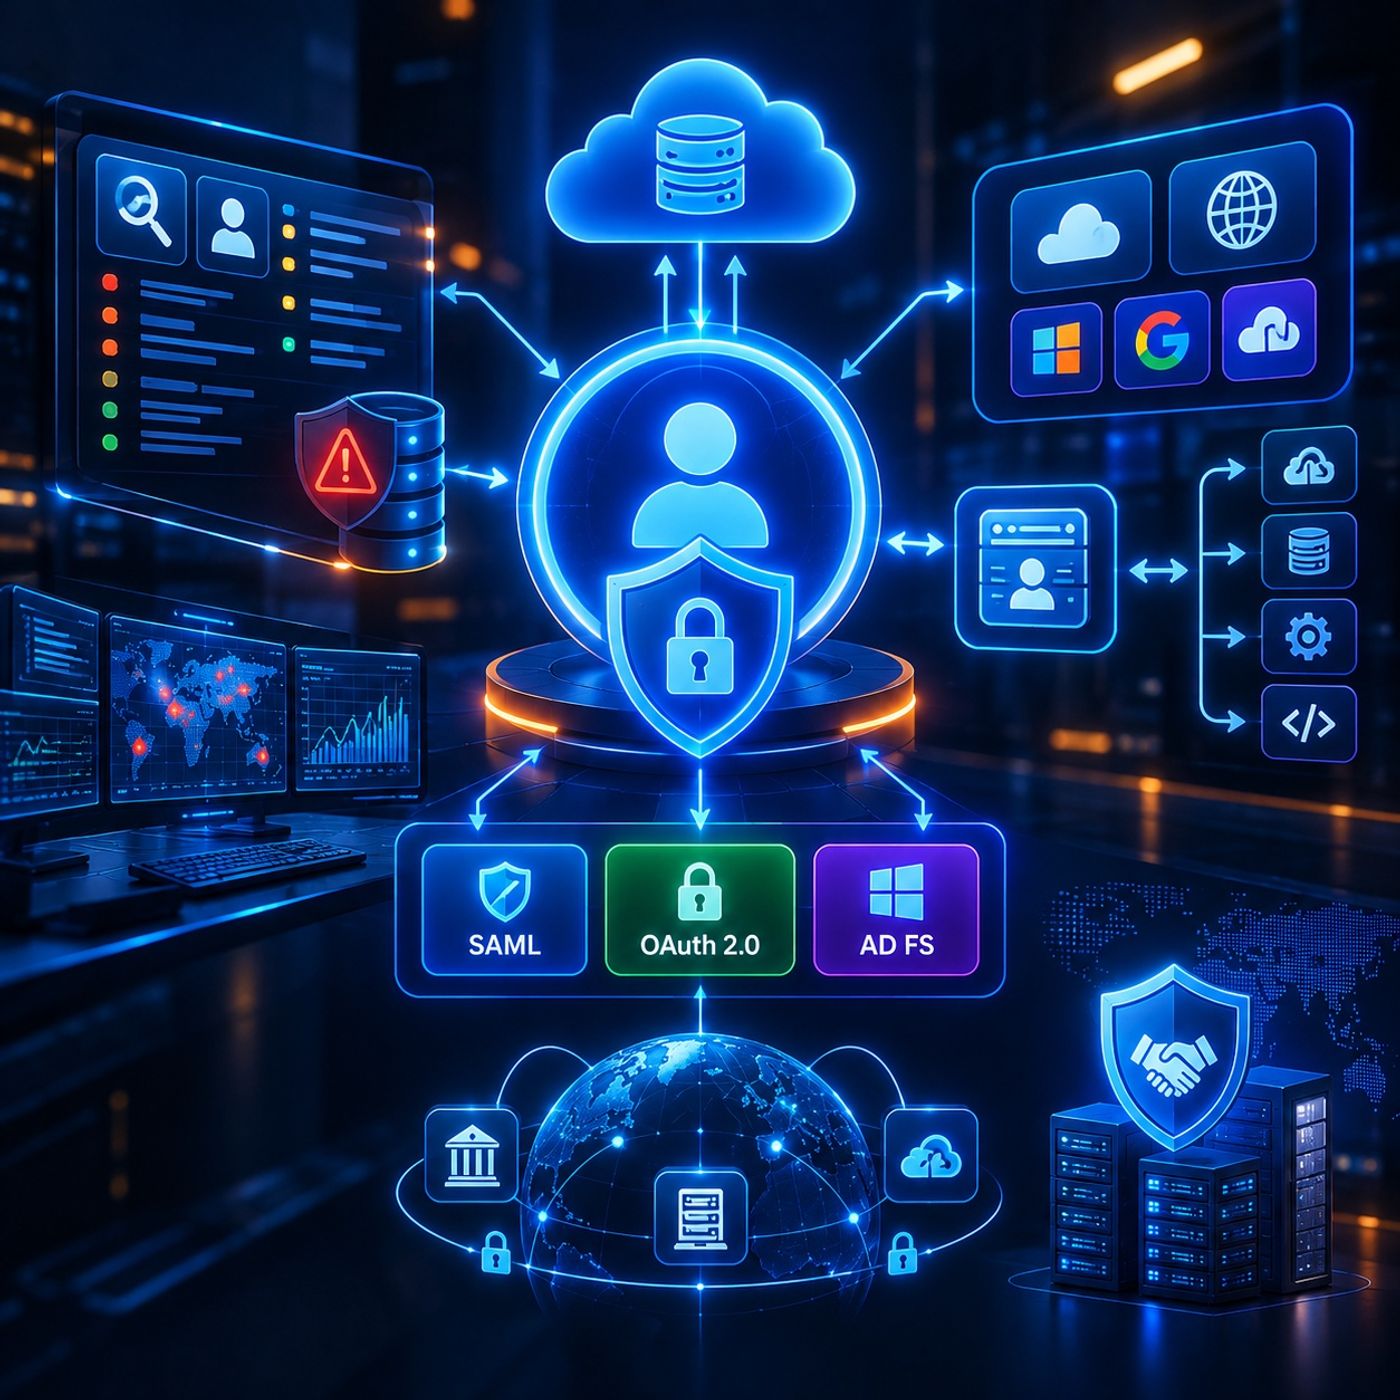
Identity Threat Detection and Federated Identity ArchitectureEpisode OverviewThis episode explores two critical areas of modern identity security: detecting attacks against identity and access management (IAM) systems and designing secure federated identity architectures.It examines how organizations use centralized security telemetry and human analysis to identify suspicious identity activity, then moves into the architecture of federated authentication, where trusted identity providers enable users to access multiple applications without maintaining separate credentials for every service.The episode also compares major federation and identity technologies, including SAML, OAuth 2.0, and Active Directory Federation Services (AD FS), while examining the security and operational risks introduced by reliance on external identity providers.Key Topics Covered1. Detecting Attacks Against Identity SystemsIdentity infrastructure generates valuable security telemetry that can reveal compromised accounts, privilege abuse, and unauthorized changes.
• IAM Log Integration: Forward authentication, authorization, account-management, and privileged-access events to a SIEM for centralized analysis.
• Privileged Account Monitoring: Track administrative authentication, privilege elevation, unusual administrative activity, and access to sensitive systems.
• Permission Changes: Monitor modifications to group memberships, roles, ACLs, and other authorization settings.
• Identity Lifecycle Events: Monitor account creation, modification, disabling, deletion, and other lifecycle changes.
• Authentication Anomalies: Investigate unusual login times, locations, devices, authentication methods, or repeated failures.
• Behavioral Analysis: Compare observed activity against established baselines to identify potentially suspicious deviations.
• Human Analysis: Automated detection can prioritize and correlate events, but experienced analysts remain important for understanding business context, distinguishing legitimate administrative activity from abuse, and investigating ambiguous patterns.
• Incident Correlation: Combine IAM telemetry with endpoint, network, application, and cloud-service logs to build a broader picture of potential compromise.
2. Federated Identity ArchitectureFederated identity allows organizations to establish trust relationships between an Identity Provider (IdP) and applications or services operated by another organization.A typical federation involves:
• Identity Provider (IdP): Authenticates the user and provides identity or authorization information to a relying application.
• Relying Party (RP): A service or application that relies on assertions or tokens from the trusted identity provider.
• User: The individual attempting to access the federated service.
• Trust Relationship: The IdP and relying party establish technical and administrative trust, including configuration of identifiers, keys, endpoints, claims, and validation requirements.
•…
Website: spreaker.com
