
Course 46 - CompTIA Cybersecurity Analyst | Episode 6: Penetration Testing, Team War Games, and Reverse Engineering
· 26 min
Show notes
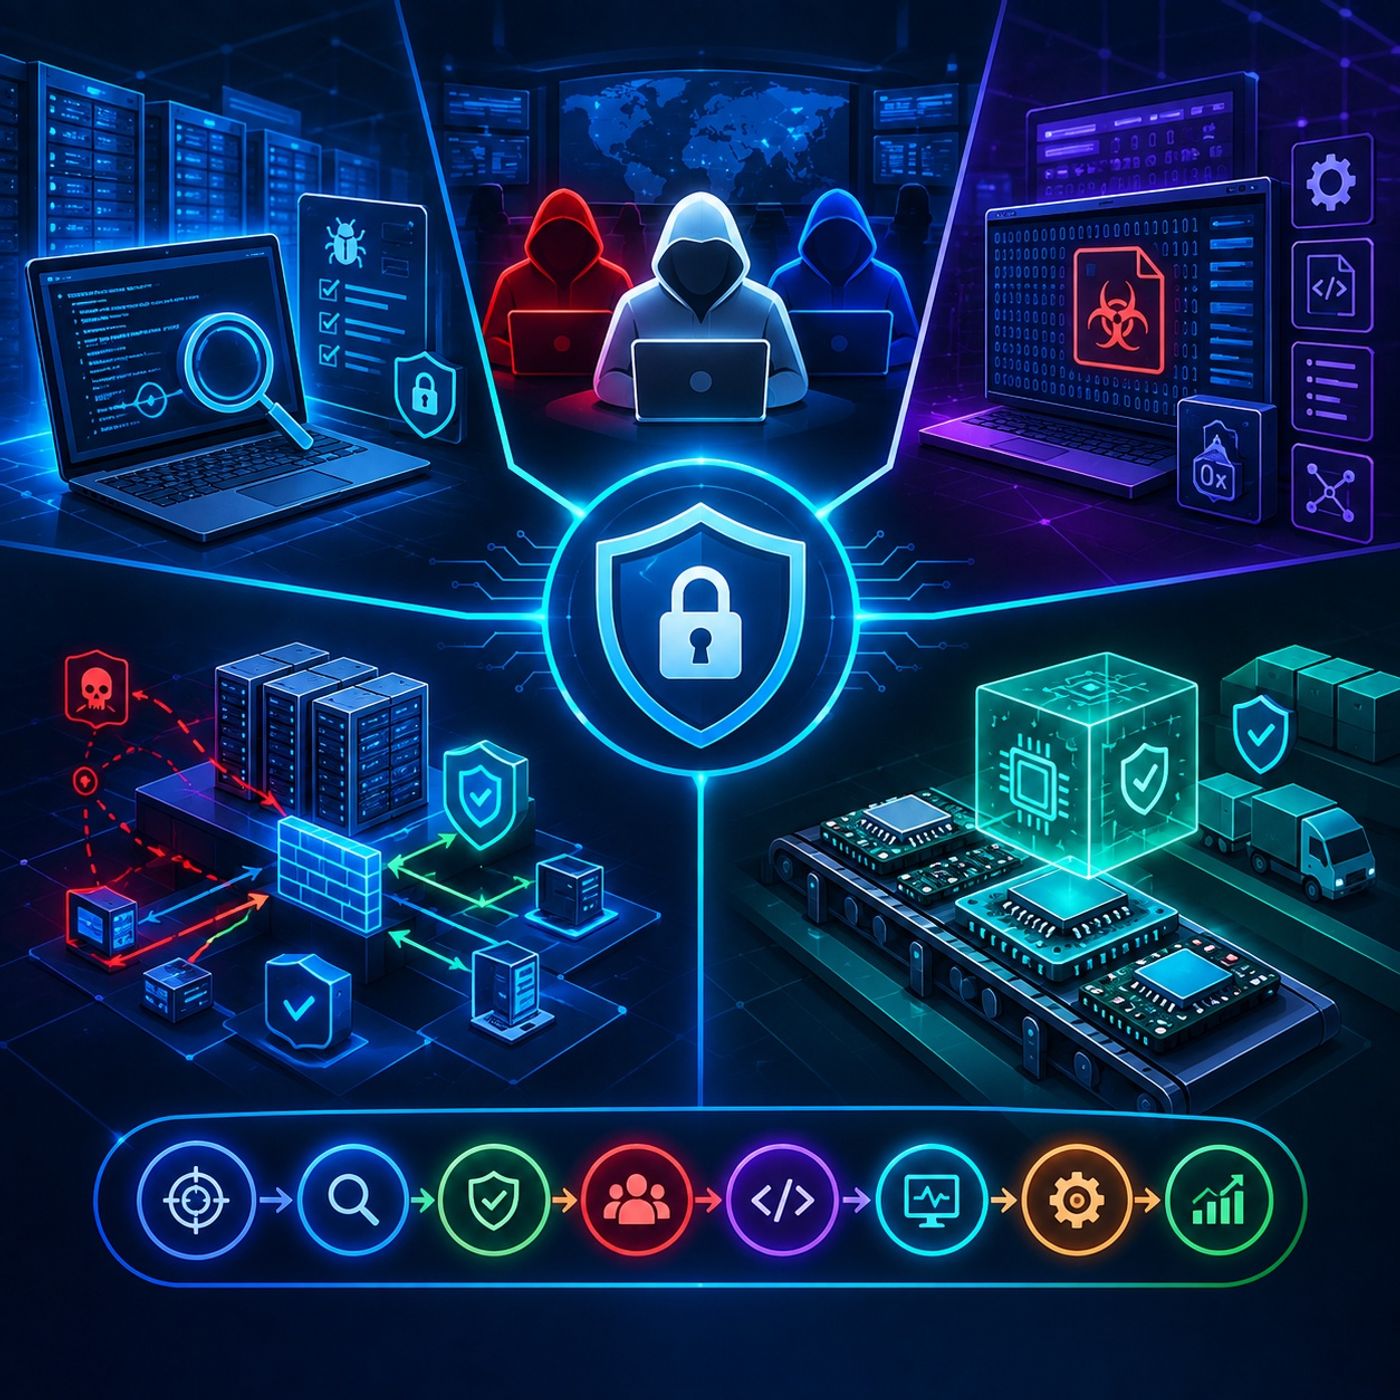
Episode OverviewThis episode explores the core methodologies used to assess, simulate, investigate, and strengthen cybersecurity defenses. It brings together three complementary areas of security operations: structured penetration testing, controlled adversary simulations, and reverse engineering for malware analysis.From evaluating an organization's external attack surface to conducting realistic Red Team and Blue Team exercises, the episode demonstrates how security professionals can identify weaknesses and validate defensive capabilities. It also examines how reverse engineering and malware analysis can reveal the behavior and internal logic of unknown binaries, while highlighting the importance of security throughout the technology supply chain.Key Topics Covered1. Penetration Testing FrameworkThe episode introduces the fundamentals of structured penetration testing and distinguishes outside-in security assessments from inside-out vulnerability management and scanning activities.It examines the four major phases described in NIST Special Publication 800-115:
• Planning — defining scope, objectives, rules of engagement, and assessment requirements.
• Discovery — gathering information and identifying systems, services, vulnerabilities, and potential attack paths.
• Attack / Exploitation — safely validating whether identified weaknesses can actually be exploited within the authorized scope.
• Reporting — documenting findings, evidence, business impact, and prioritized remediation recommendations.
The episode emphasizes that effective penetration testing is not simply about finding vulnerabilities. Clear reporting and meaningful risk prioritization are essential for helping management understand exposure and allocate remediation resources effectively.2. Security Exercises and Cybersecurity War GamesThe episode then moves from individual security assessments to live-fire security exercises, where organizations simulate realistic attacks and defensive responses inside controlled environments.These exercises commonly divide participants into three primary roles:
• Red Team — simulates adversarial activity through authorized reconnaissance, attack simulation, and exploitation.
• Blue Team — protects the environment by hardening systems, monitoring activity, detecting attacks, containing threats, and restoring affected services.
• White Team — provides neutral coordination by defining the rules, managing the exercise environment, resolving disputes, and ensuring that the simulation remains within its approved boundaries.
Virtualized and isolated environments make these exercises especially valuable because organizations can test their people, processes, technologies, and incident-response capabilities without exposing production systems to unnecessary risk.3. Reverse Engineering and Malware AnalysisThe final section examines how security researchers investigate unknown or suspicious compiled binaries.The episode compares two complementary…
Website: spreaker.com
