
Course 47 - SCADA Security Architect (CSSA) | Episode 11: Identity, Authorization & Access Control
· 21 min
Note de episod
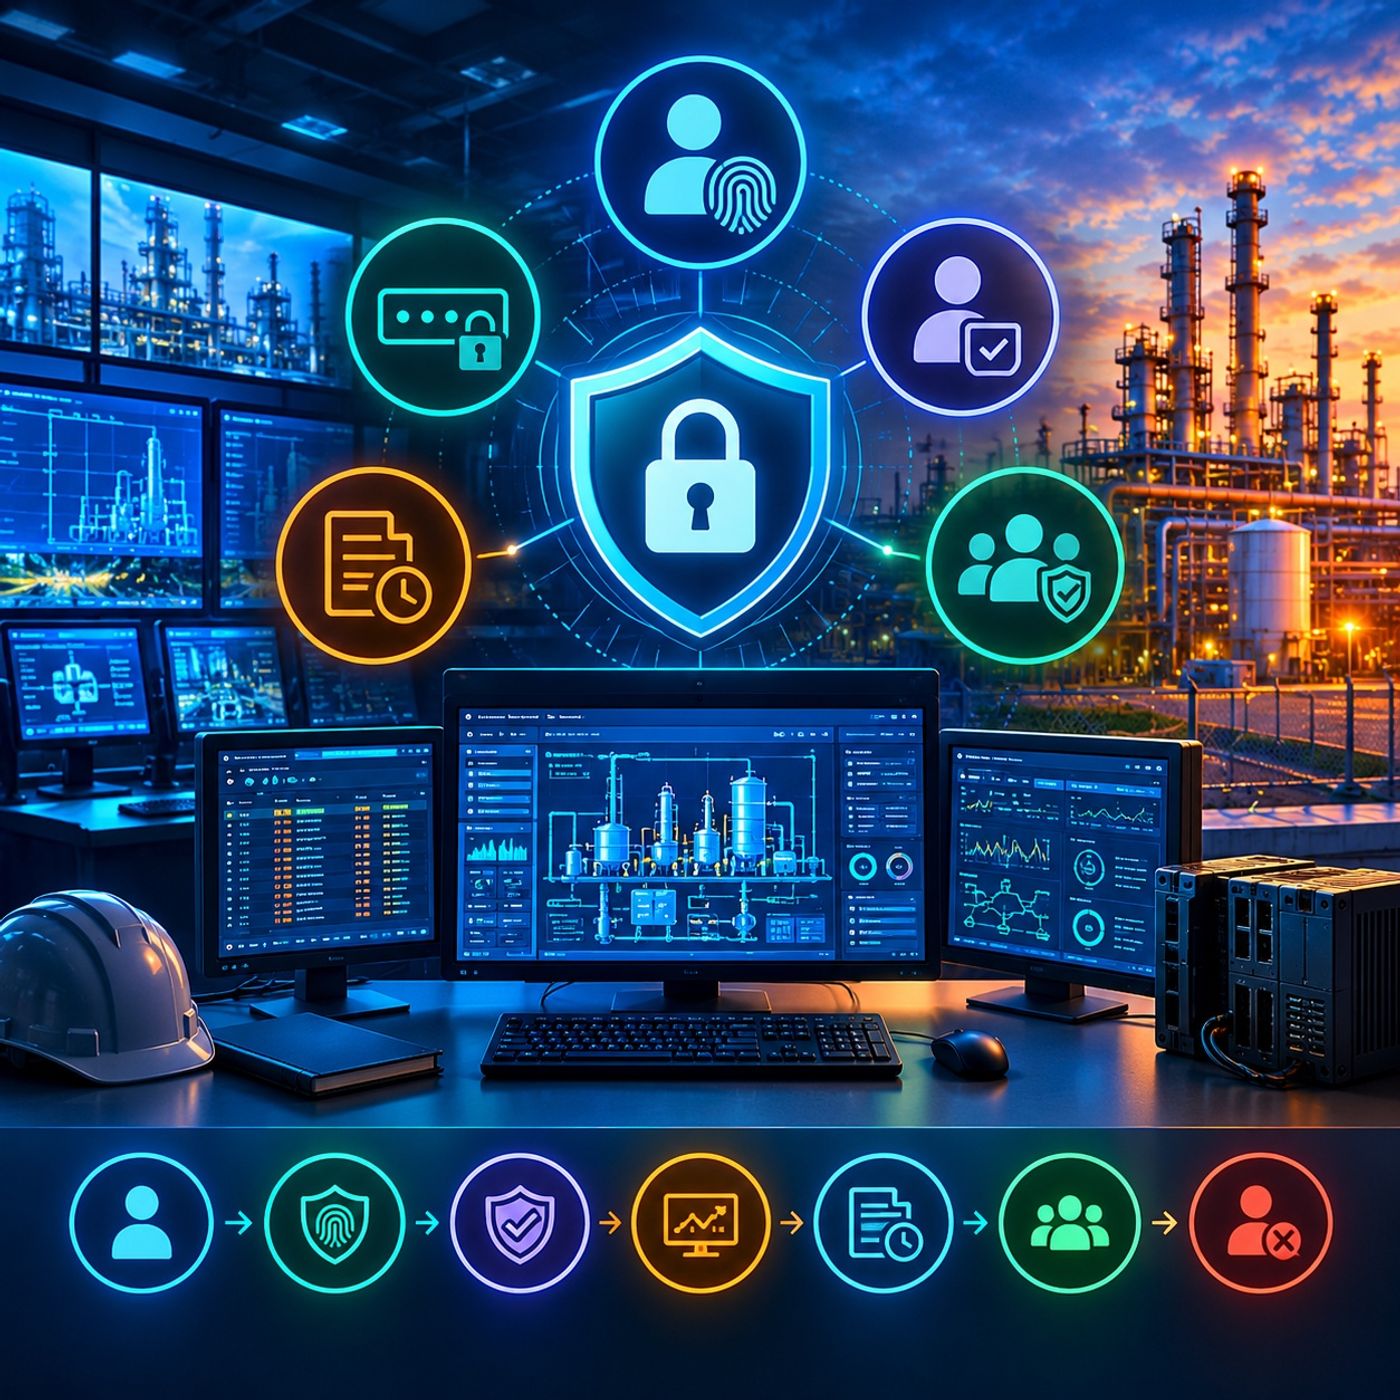
Securing Industrial Systems: Identity, Authorization & Access ControlEpisode OverviewThis episode explores identity management and access control in Industrial Control Systems (ICS) and SCADA environments. It examines the IAAA security framework and access control models used to ensure that users and systems receive only the permissions necessary to perform their authorized tasks.Key Topics Covered1. Identity, Authentication, Authorization, and Accountability (IAAA)
• Identification: Establishing a unique identity for each user, device, or system.
• Authentication: Verifying identities through passwords, multifactor authentication, certificates, or other supported mechanisms.
• Authorization: Determining which resources and operations an authenticated identity may access.
• Accountability: Recording and reviewing activities through logs and audit trails to support monitoring and investigations.
2. Access Control Models
• Role-Based Access Control (RBAC): Assigning permissions according to job functions and operational responsibilities.
• Group-Based Access Control (GBAC): Managing access through membership in defined user groups, where supported by the system.
• Location-Based Access Control (LBAC): Applying access restrictions based on physical or logical location, depending on the implementation.
• Areas of Responsibility: Dividing operational duties and system access boundaries to reduce unauthorized actions and excessive privileges.
3. Applying Access Controls in ICS/SCADA
• Enforcing least privilege for operators, engineers, administrators, and external vendors.
• Separating duties between system operation, configuration, and security administration.
• Restricting access to critical controllers, engineering workstations, and management interfaces.
• Monitoring authentication events, permission changes, and privileged activities.
• Reviewing accounts regularly and promptly revoking access when responsibilities change.
Key Takeaways
• Identification, authentication, authorization, and accountability are distinct but complementary security functions.
• Access control models help organizations apply consistent, role-appropriate permissions.
• Least privilege and separation of duties reduce the risk of accidental or unauthorized changes.
• Audit logs support accountability, incident detection, and forensic investigation.
• Industrial access controls must protect critical operations without compromising safety or availability.
Access Control Workflow: Identify → Authenticate → Authorize → Monitor → Record Activity → Review Permissions → Revoke or Adjust Access
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
Get the books of the CyberCode Academy podcast:
📚 The book series: 416 lessons, 12 books, hundreds of original diagrams: security, networking and programming.
https://cybercodeacademy.gumroad.com/
Site: spreaker.com


