
Notas do episódio
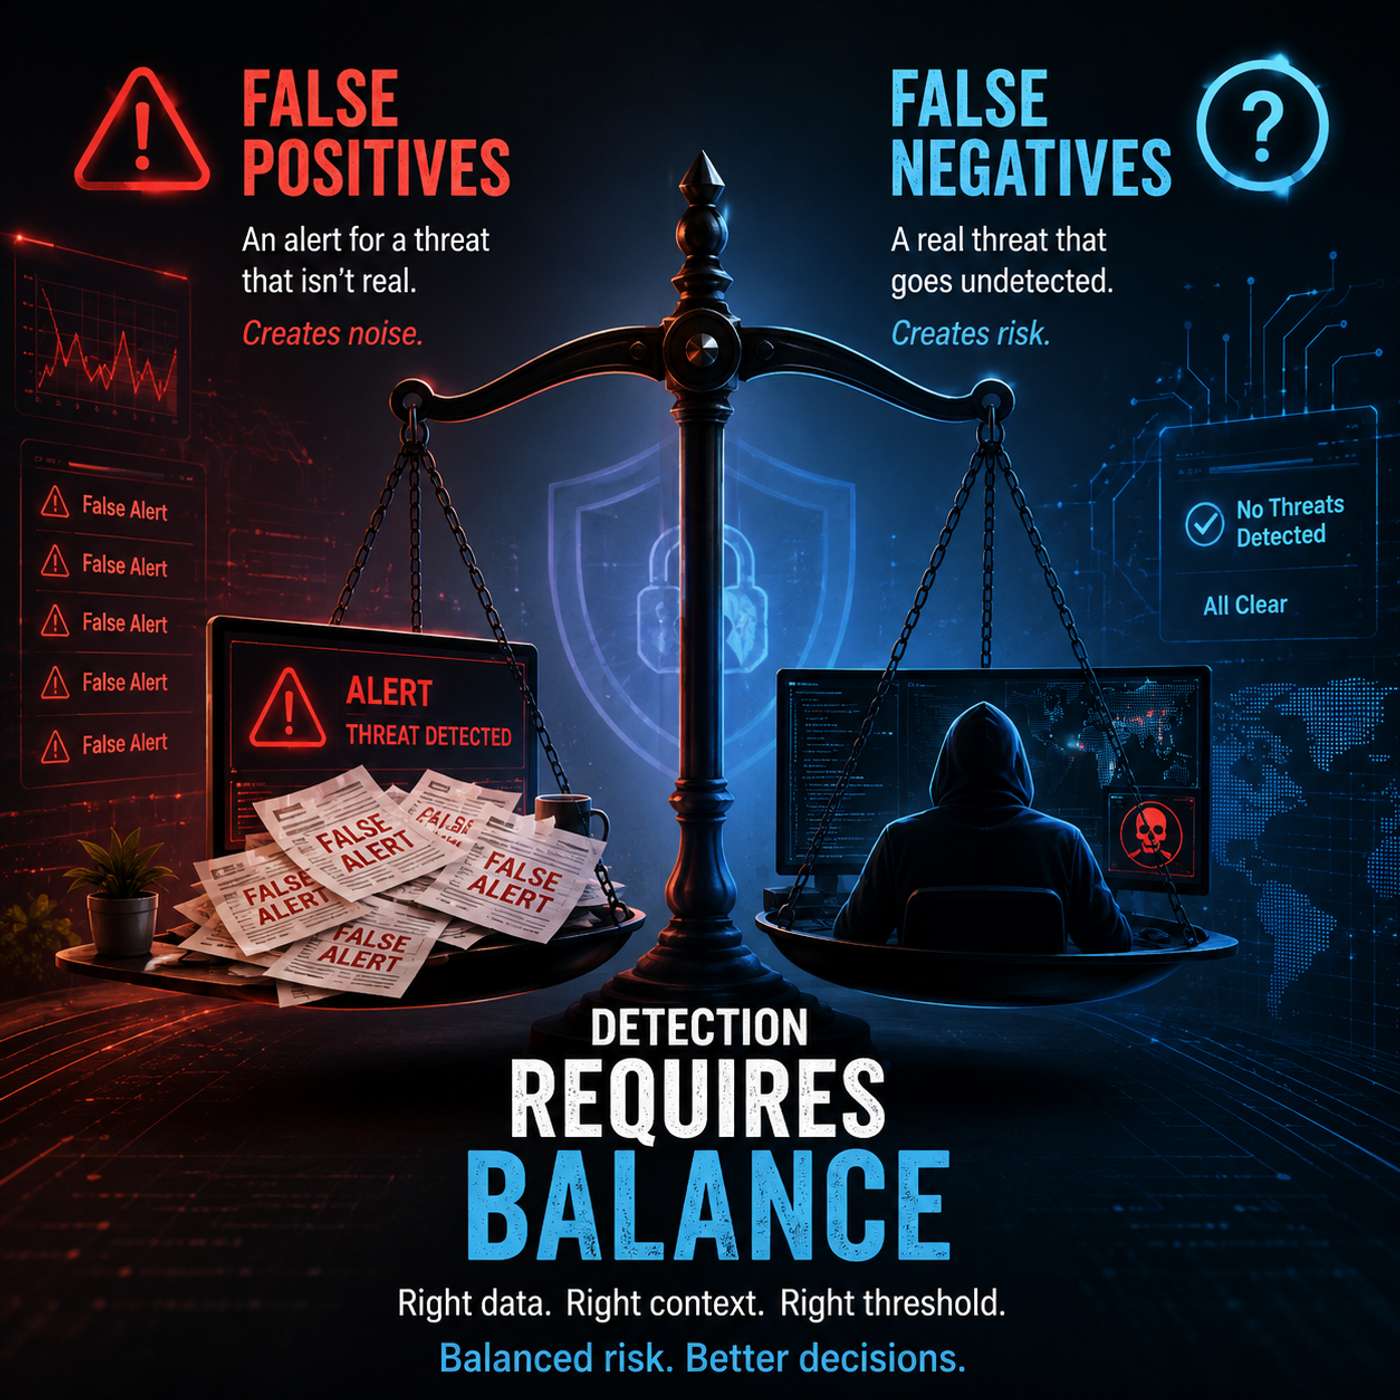
A false positive occurs when a security control reports malicious activity that is not actually present, while a false negative occurs when genuine malicious activity is missed. Certification exams may ask candidates to identify these outcomes or explain the tradeoff created when detection thresholds are adjusted. A rule that alerts on every administrative script may create excessive false positives, while a rule that requires several severe conditions may overlook a real attack. Defenders should tune controls using validated data, asset criticality, threat context, and acceptable risk…
Site: share.transistor.fm
