
Shownotes
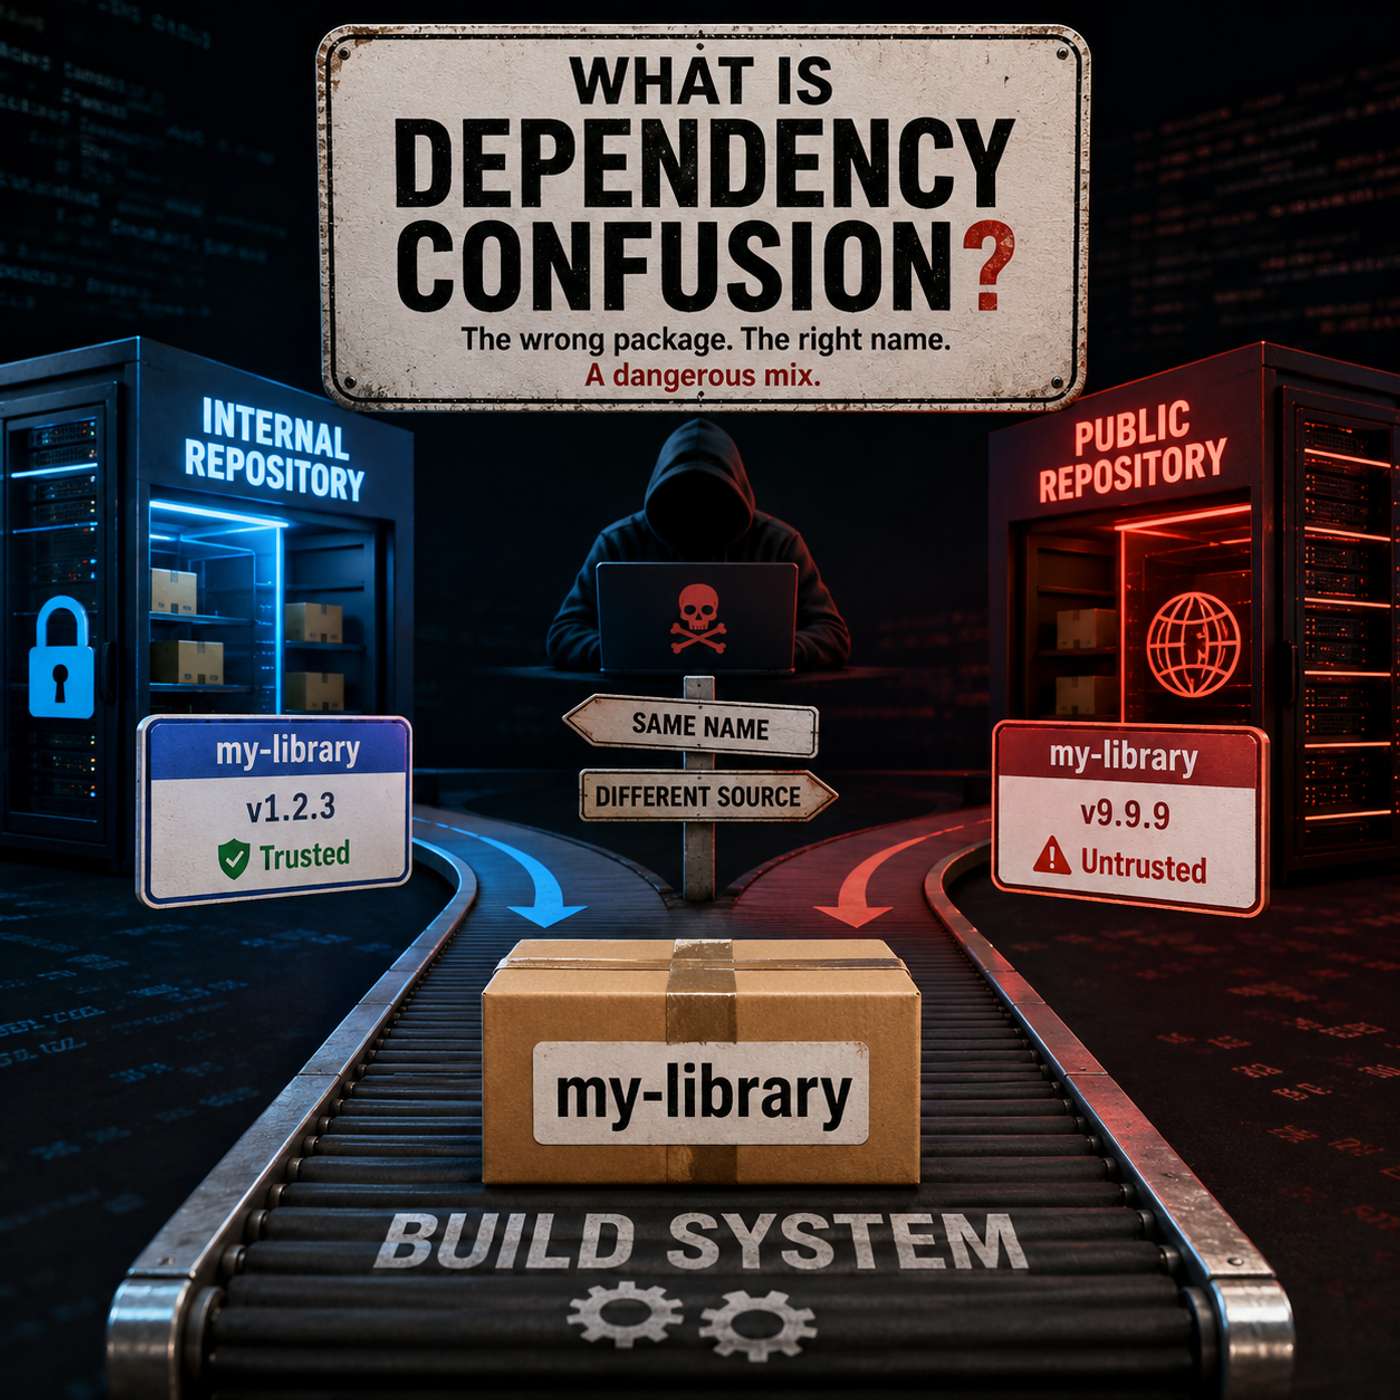
Dependency confusion occurs when a software build or package-management system retrieves an attacker-controlled public package instead of the organization’s intended internal dependency. Certification exams may describe identical package names in private and public repositories and ask candidates to identify the software supply-chain risk. An attacker may publish a package with the expected internal name and a version number that causes automated tools to select it during installation or compilation. Defenses include private package namespaces, repository-priority controls, package…
Website: share.transistor.fm
