
Shownotes
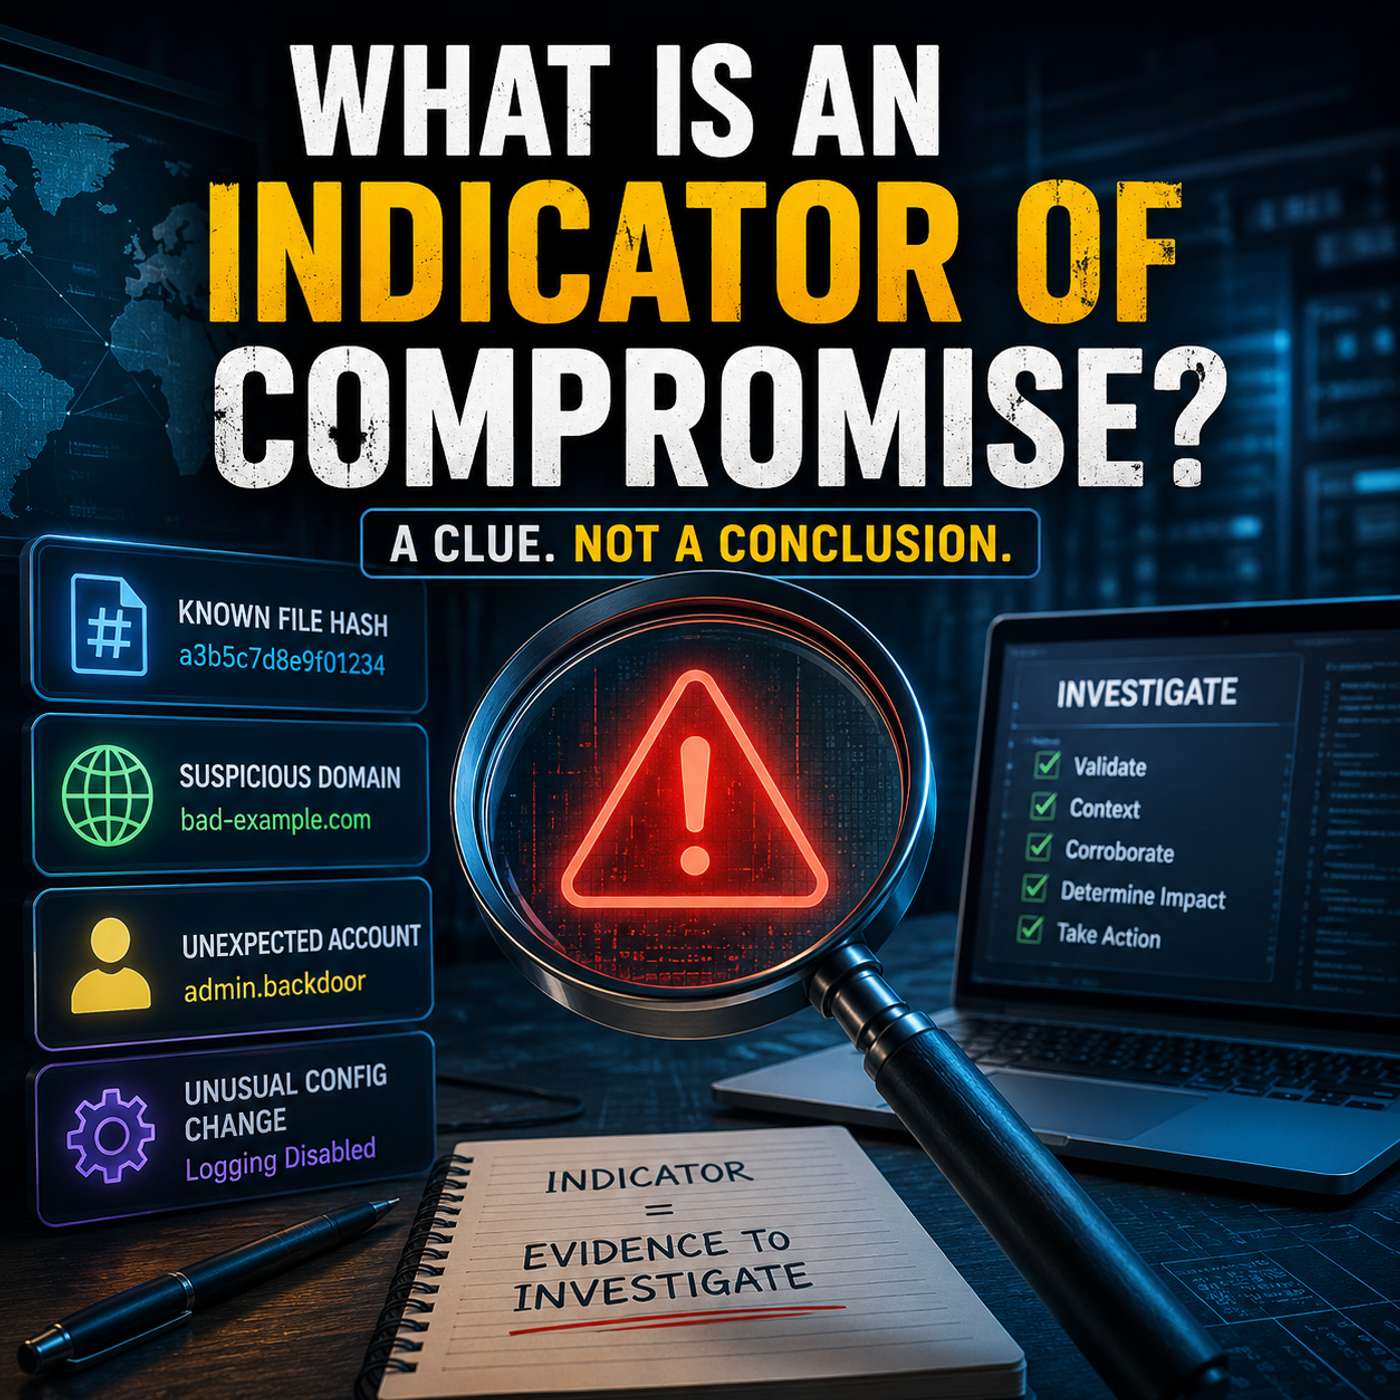
An indicator of compromise is an observable clue suggesting that malicious activity may have occurred within a system or environment. Certification exams may present a suspicious file hash, unfamiliar domain, unexpected account, altered configuration, unusual process, or unauthorized network connection and ask candidates to classify it as an indicator requiring investigation. An indicator is not automatic proof of an incident because legitimate activity may produce similar evidence, and attackers may change their tools or infrastructure. Analysts should combine multiple indicators with…
Website: share.transistor.fm


