
Show notes
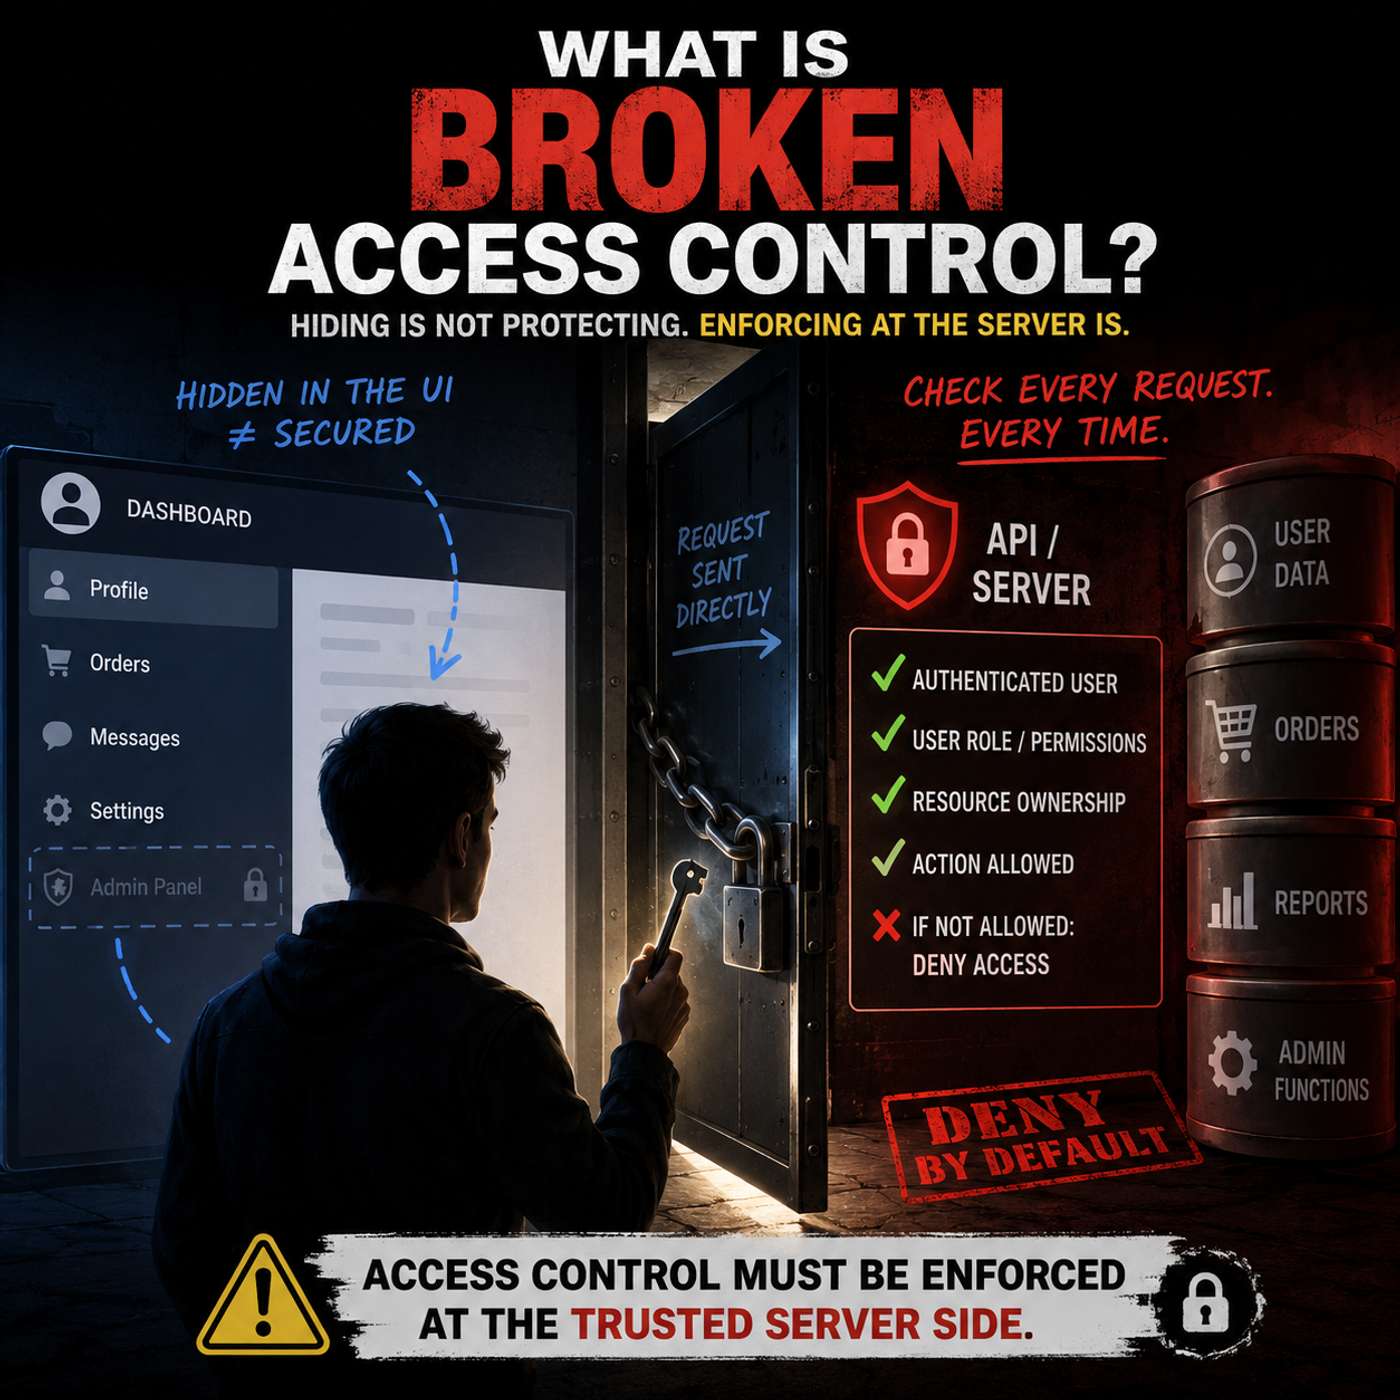
Broken access control occurs when an application fails to enforce what an authenticated or unauthenticated user is permitted to view, change, create, or delete. Certification exams may present a user who changes a record identifier, enters a hidden web address, or modifies a request and then gains access to another person’s data. Hiding a button or menu option does not protect the underlying function because attackers can send requests directly. Applications must perform authorization checks on the server for every protected action and resource. Role-based permissions, ownership validation…
Website: share.transistor.fm
