
Show notes
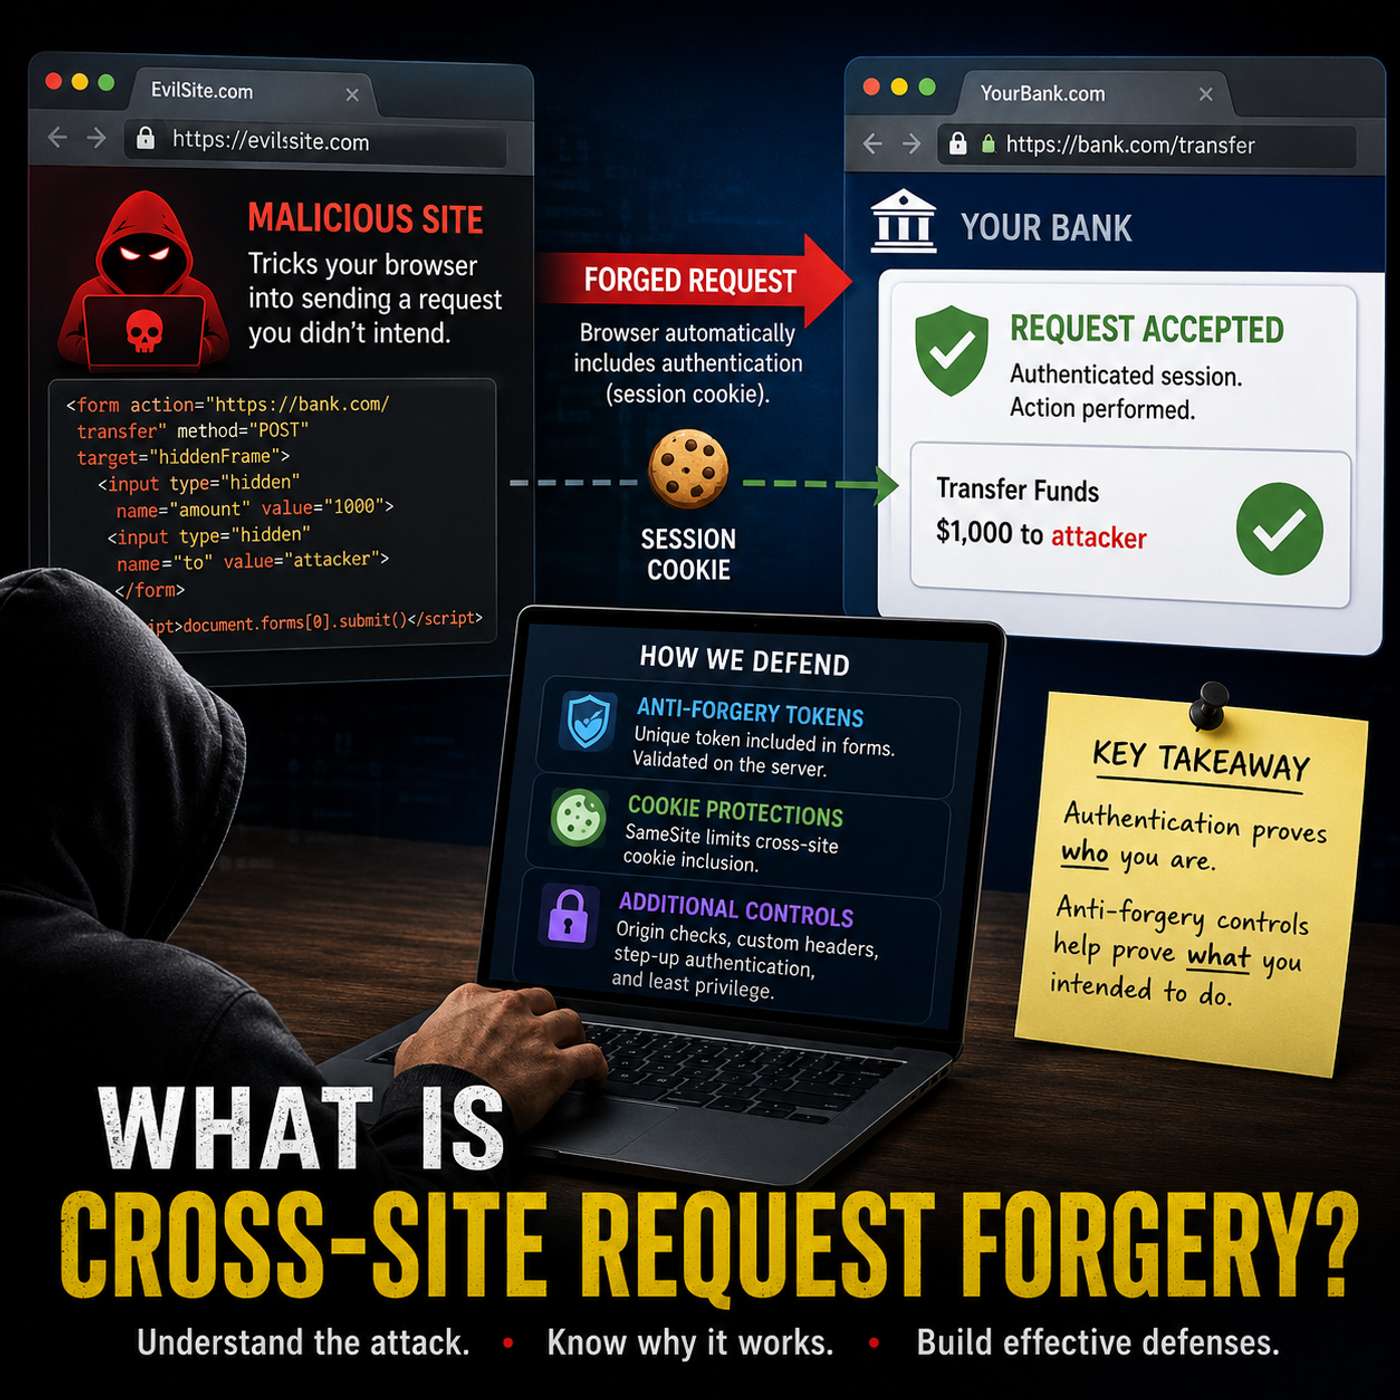
Cross-site request forgery occurs when an attacker causes a logged-in user’s browser to submit an unwanted request to a trusted application. Certification exams may describe a victim visiting a malicious page while already authenticated to another service and ask candidates to identify why the second application accepts the request. Because the browser automatically includes session cookies, the application may believe the request was intentionally submitted by the user. An attacker could attempt to change an email address, transfer funds, modify settings, or perform another authorized…
Website: share.transistor.fm
