
Show notes
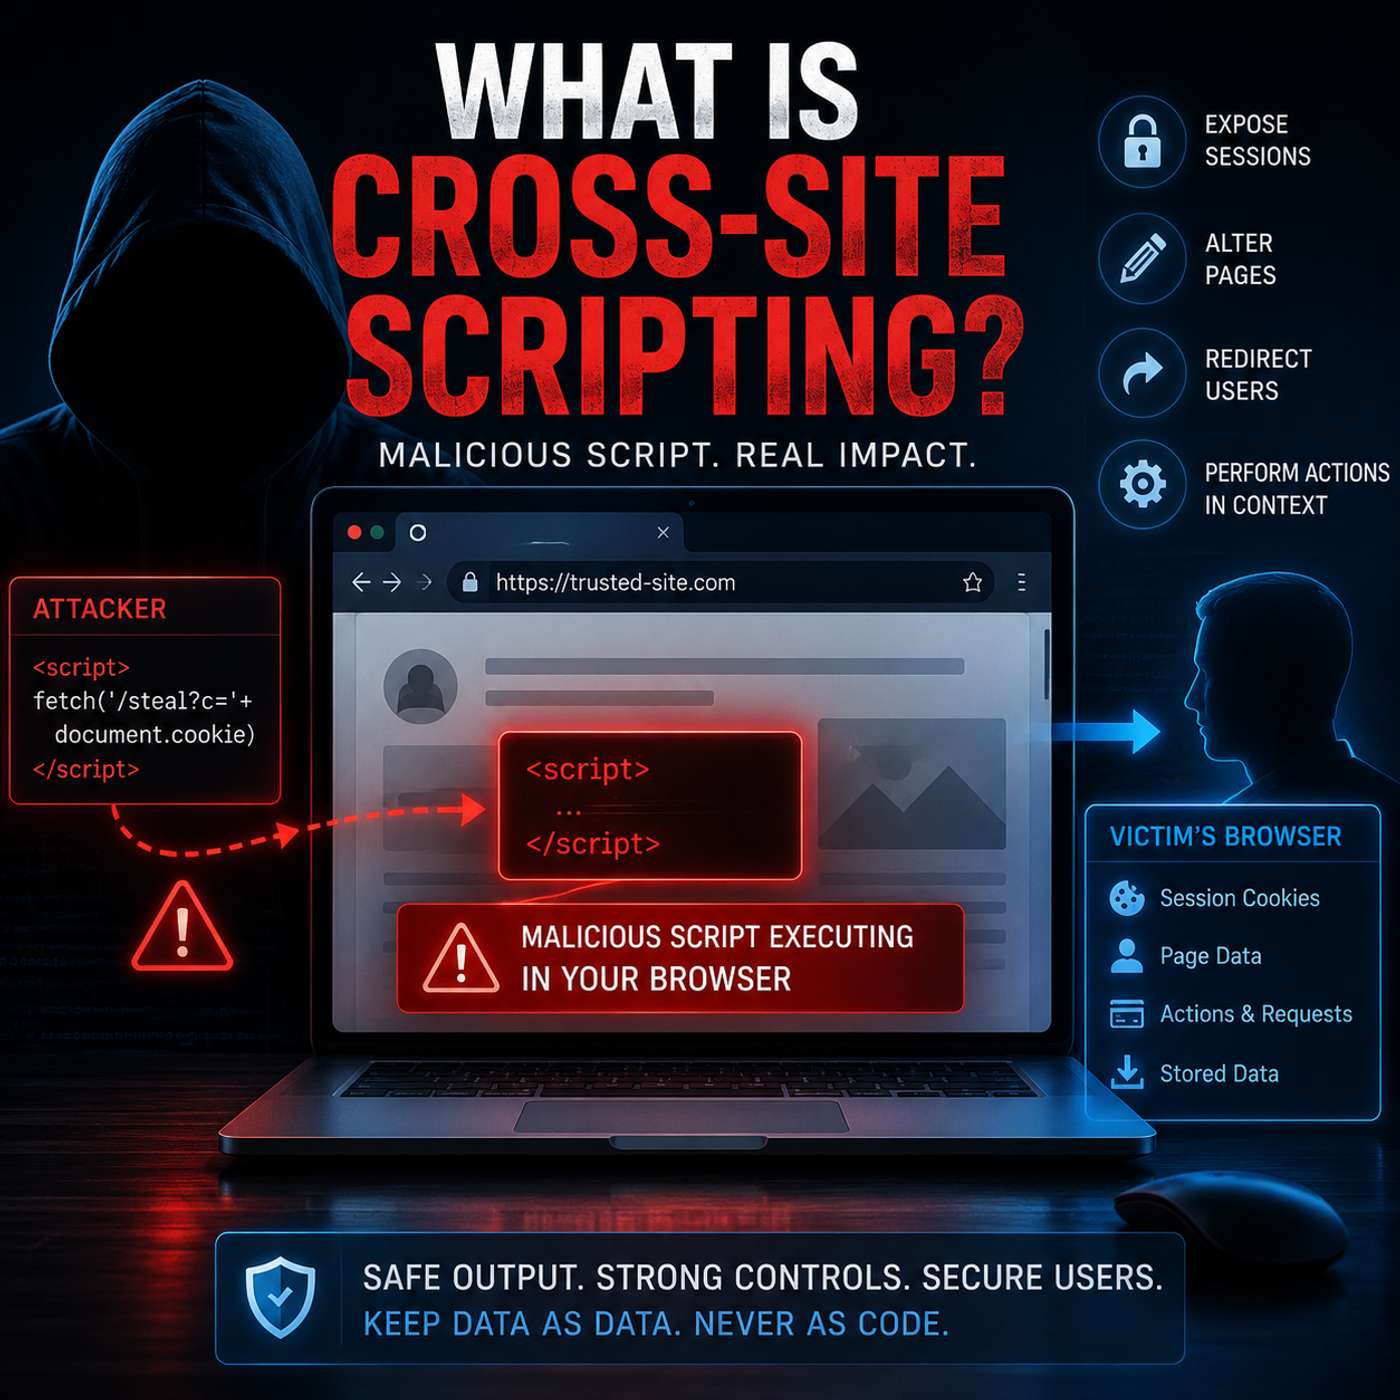
Cross-site scripting, or XSS, occurs when an application allows malicious script content to execute in another user’s browser within the context of a trusted website. Certification exams may ask candidates to distinguish stored, reflected, and document-based forms of XSS or identify the appropriate defensive control. A stored attack saves malicious content in a database or page, while a reflected attack returns crafted input in an immediate response. Successful exploitation may expose session information, alter displayed content, redirect users, capture input, or perform actions using the…
Website: share.transistor.fm
