
Show notes
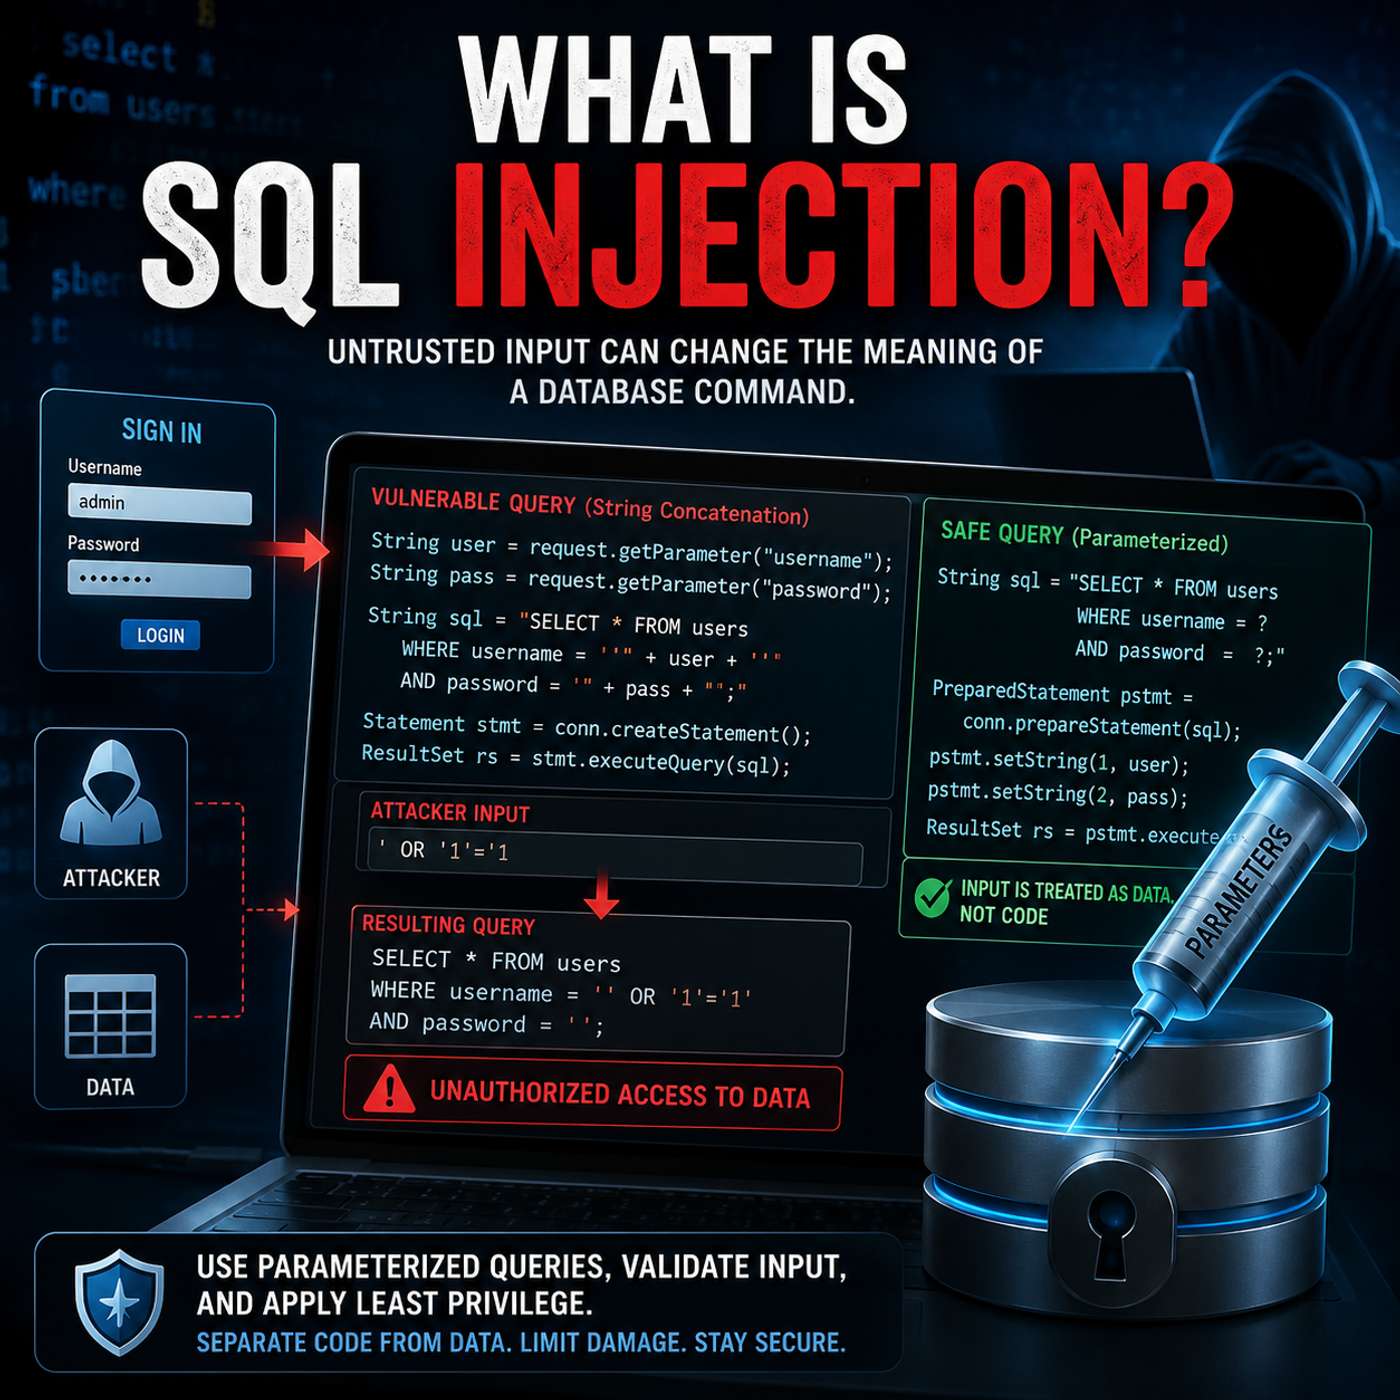
SQL injection occurs when untrusted input changes the structure or meaning of a database command created by an application. Certification exams may describe login forms, search fields, or application programming interfaces that place user input directly into a query and ask candidates to identify the vulnerability or select the strongest defense. An attacker may craft input that reads restricted records, bypasses authentication, alters information, or deletes database content. Parameterized queries and prepared statements separate data from executable instructions and are primary protections…
Website: share.transistor.fm
